Qualys today announced the expansion of its Global mROC Alliance, adding technology partners that cover parts of the attack surface traditional tools struggle to measure. NowSecure is one of them. With our connector, security teams that run their risk program in Qualys Enterprise TruRisk Management (ETM) can now see their mobile apps alongside their servers, cloud workloads and devices, with each app scored by TruRisk. The connector also fits our Agentic AI Data Partner Program, which makes NowSecure mobile app risk intelligence available inside security platforms.
Why Mobile Apps Keep Falling Out of the Risk Picture
Mobile apps handle some of an organization's most sensitive activity. They process logins, payments, health records and corporate data, and they connect to the same back-end systems your risk program already protects.
Even so, mobile app findings rarely make it into the enterprise risk view. They usually live in a separate tool, owned by a separate team, and scored on a separate scale. A security leader working in ETM can weigh a critical server vulnerability against an exposed cloud workload, but the customer-facing app calling the same APIs isn't part of that comparison. When teams set remediation priorities, mobile tends to drop out because no one can see where it ranks.
How the Integration Works
The NowSecure connector sends mobile app data from NowSecure Platform into Qualys ETM, and ETM does the scoring. Setup has three steps:
- Connect. Generate an API token in the NowSecure Platform and add it to the NowSecure connector in Qualys ETM.
- Sync. The connector imports mobile app asset records and their vulnerability findings from NowSecure into ETM on the schedule you set.
- Prioritize. ETM removes duplicates, normalizes the data into its standard model, enriches each finding with Qualys threat intelligence, and calculates a TruRisk score for every app.
What Changes for Your Security Team
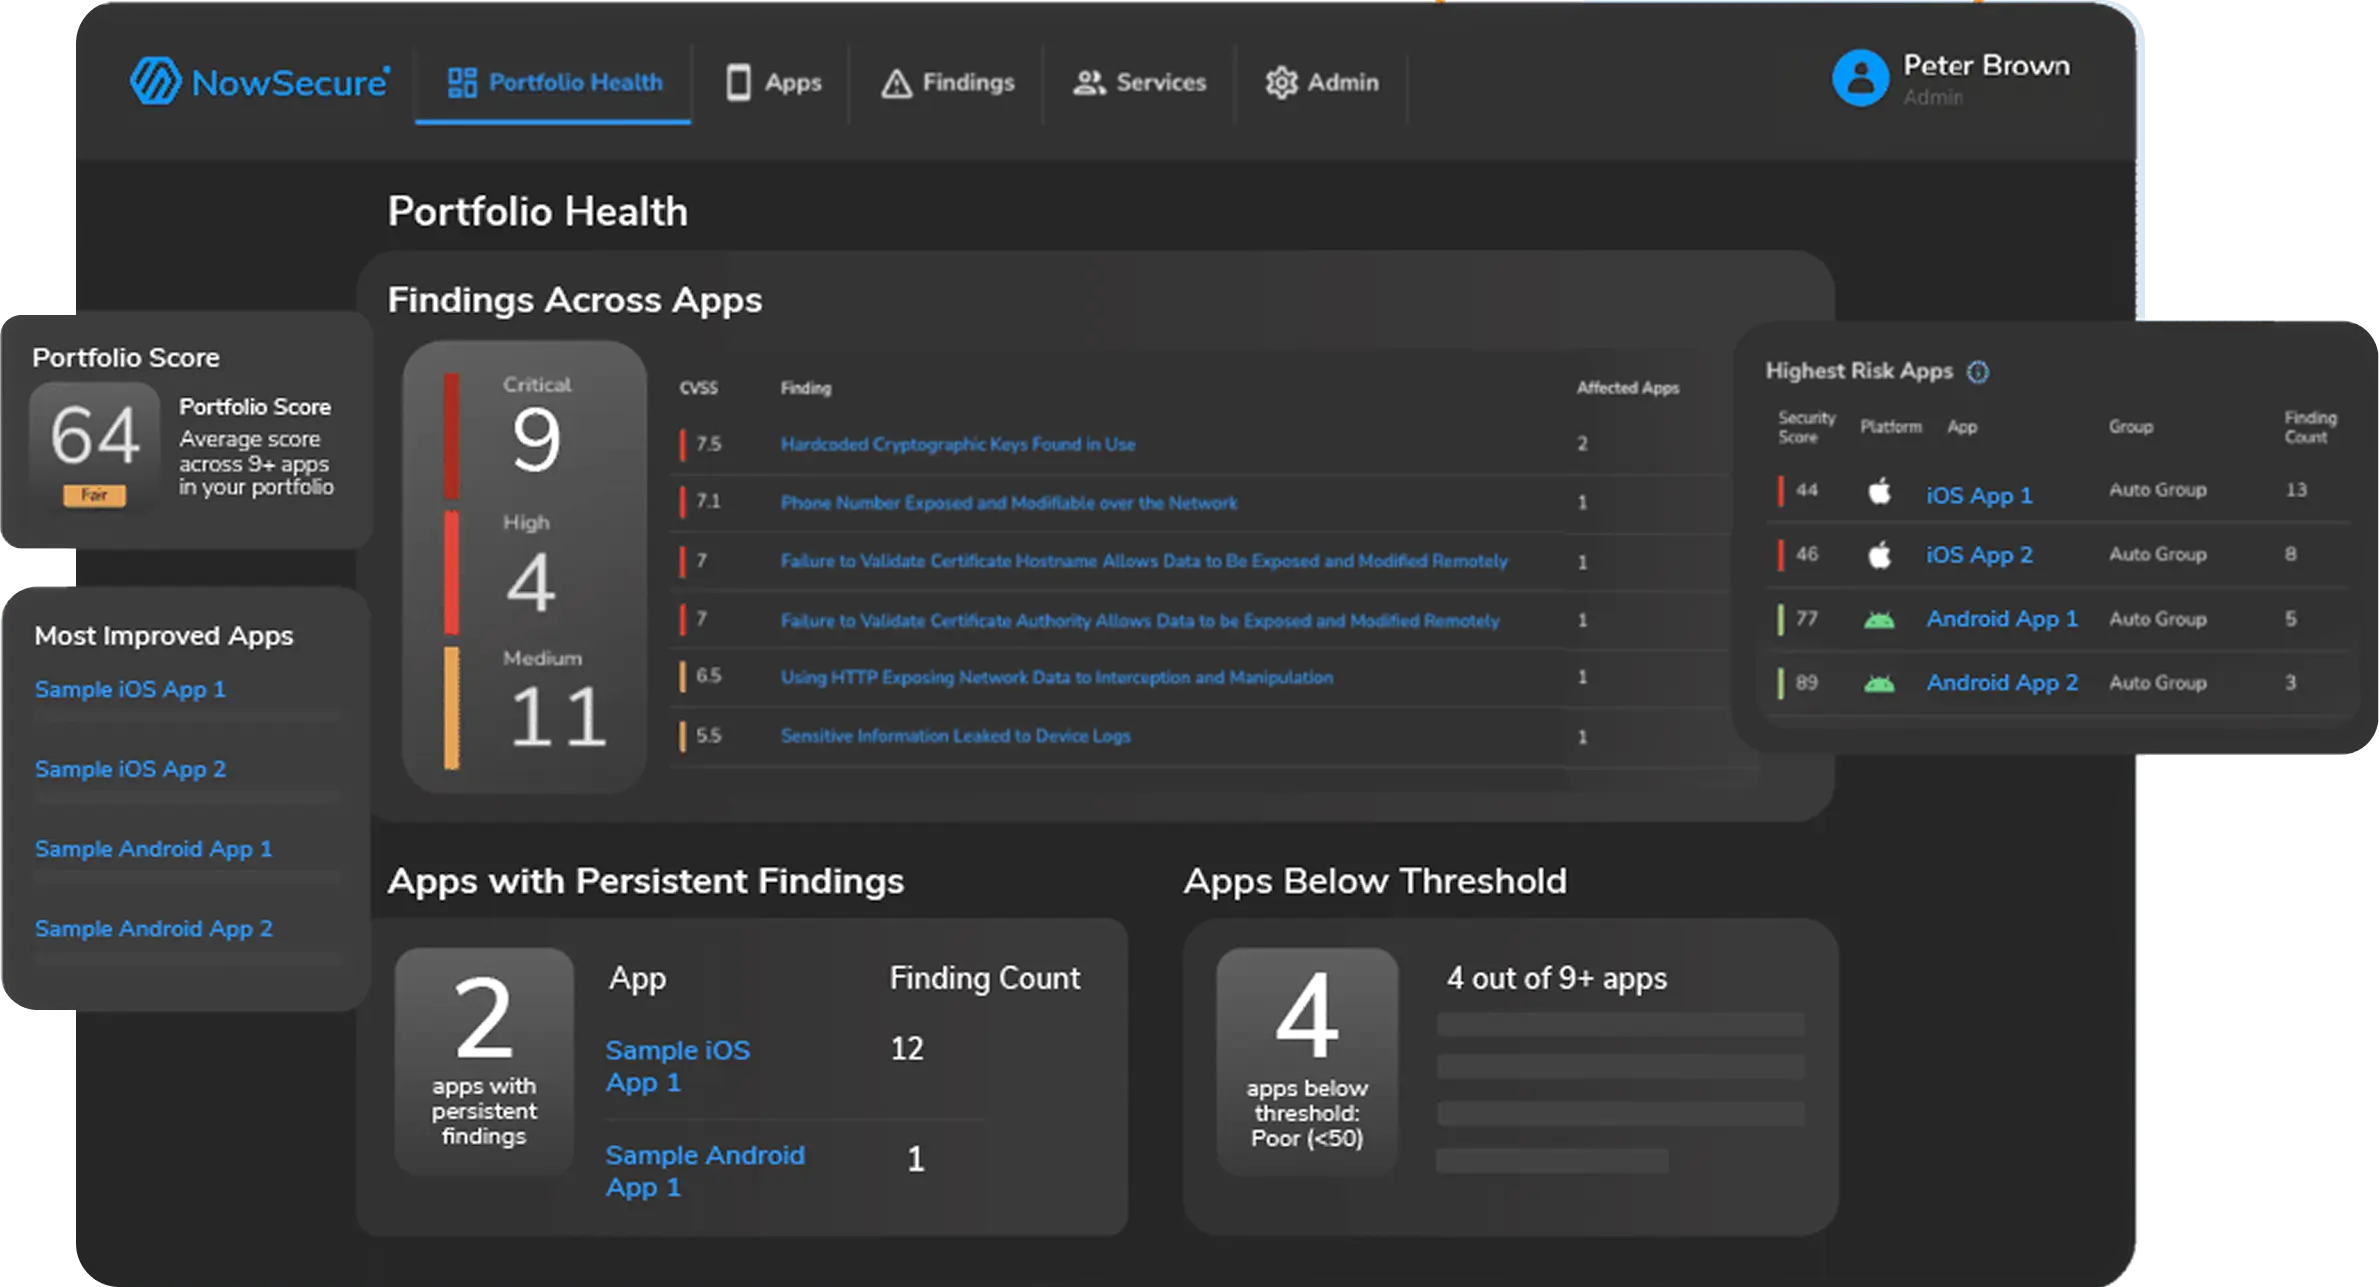
The first change is simple: your mobile apps show up in the ETM inventory next to servers, mobile devices, cloud workloads, and containers. When the team decides what to fix first, mobile is finally part of the conversation.
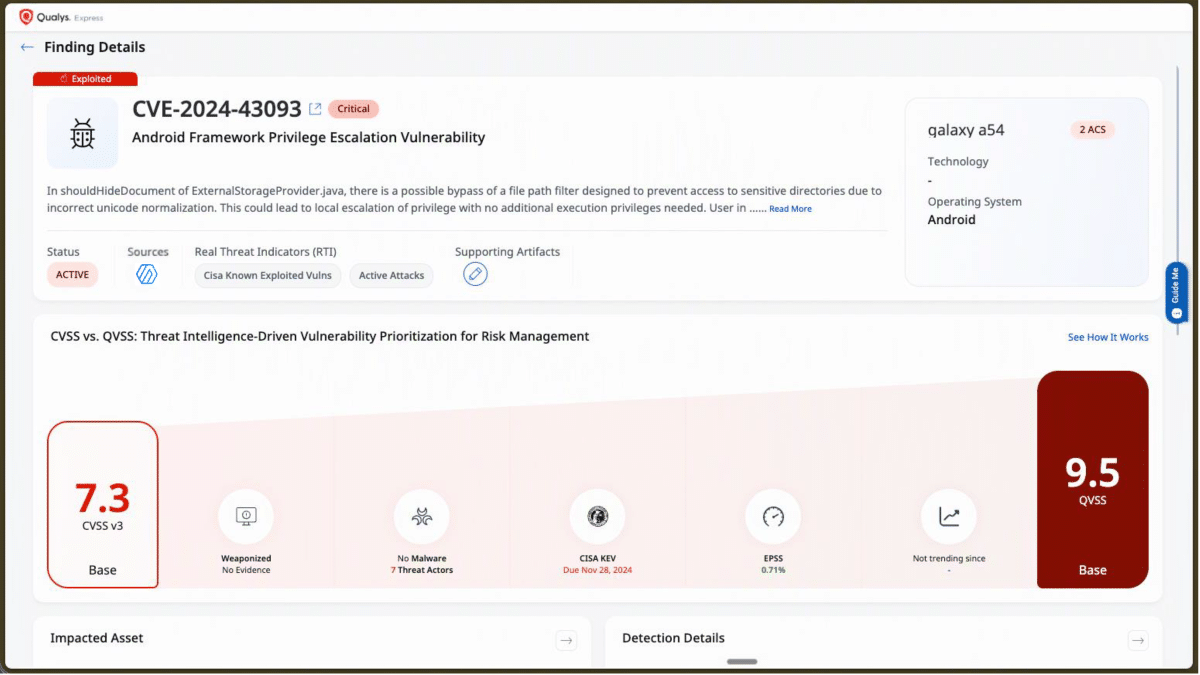
Qualys threat intelligence rescores each finding, so an issue under active attack ranks higher than its base score suggests.
Prioritization also gets sharper. Qualys enriches NowSecure findings, including issues that don’t have a CVE, with threat intelligence such as the CISA Known Exploited Vulnerabilities catalog and EPSS, then rescores them with QVSS. A mobile finding that attackers actively exploit rises above one they don’t, the same way it would for any other asset.
Each app ends up with a single TruRisk score that rolls up asset criticality and its NowSecure findings. Because the score uses the same scale as everything else in ETM, you can explain mobile app risk to leadership in the terms they already use for the rest of the environment.
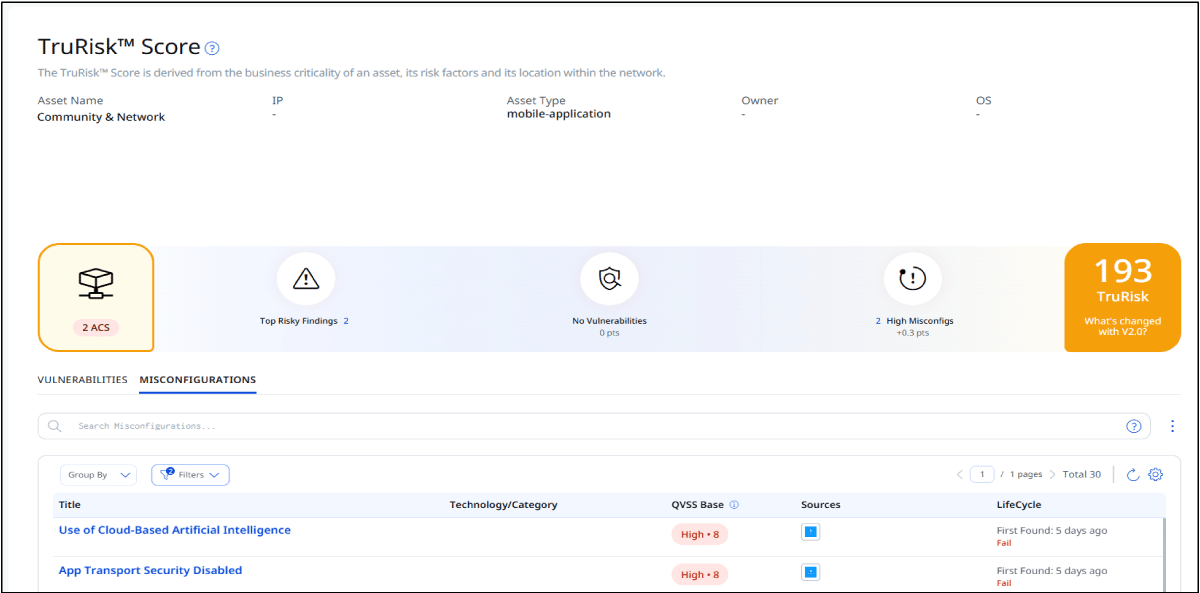
Each mobile app gets one TruRisk score, built from its asset criticality and its findings.
AppSec and security operations also stop working from separate reports. Mobile findings land in the ETM workflows your SecOps team already runs, which makes mobile risk part of the Risk Operations Center.
Where the Findings Come From
TruRisk can only rank what it receives, so the quality of the underlying findings matters. NowSecure tests mobile apps the way they actually run. We analyze the app binary, including the third-party SDKs and AI components bundled inside it. We also test how the app behaves at runtime on real iOS and Android devices, including what data it sends out and where it goes. That surfaces vulnerabilities and risky behavior that don’t show up in source code alone.
That focus is also what NowSecure adds to the alliance’s mobile coverage. Device-focused tools report on the phone and its operating system. NowSecure reports on the app itself: the code your team ships and the third-party code that ships with it. The same app-level intelligence also powers NowSecure MARI, which helps teams vet the third-party apps their workforce uses.
Get Started
If your team already uses Qualys ETM, the NowSecure connector is available in the Qualys Connector Marketplace. Setup takes a NowSecure API token and the ETM setup wizard, and the Qualys NowSecure connector guide walks through each step.
If you’re new to NowSecure and want to see how mobile app security testing would feed your ETM program, get a demo.

“When the team decides what to fix first, mobile is finally part of the conversation.”