Pentesting as a Service
NowSecure Pentesting as a
Service (PTaaS)
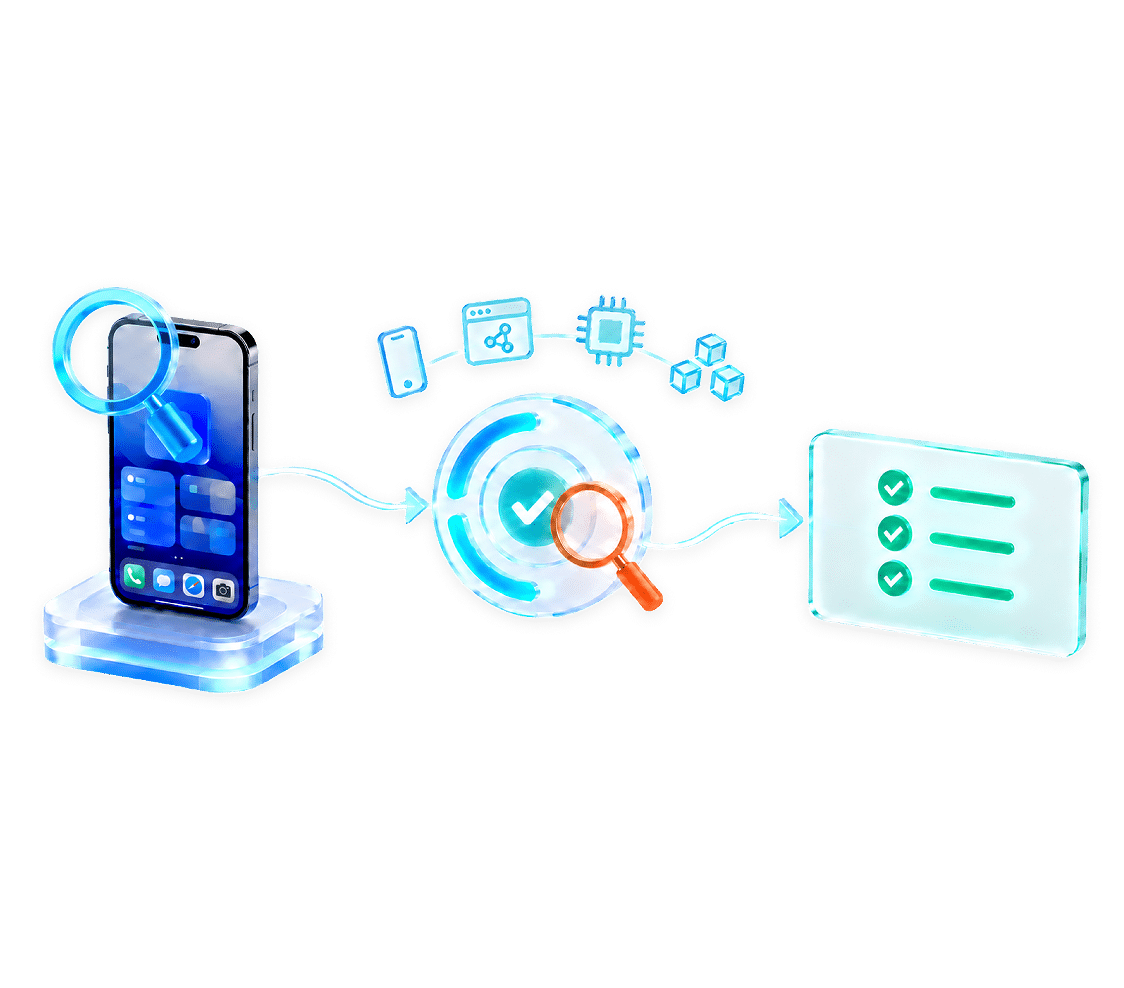
The only purpose-built platform for risk management of mobile apps, over-the-top apps, web/API, embedded apps, and 3rd party components. NowSecure PTaaS takes your traditional pentesting to the next level by pairing continuous or automated testing with world-class expert-led testing.
What is PTaaS?
Benefits of NowSecure PTaaS
Rapid Results Integration
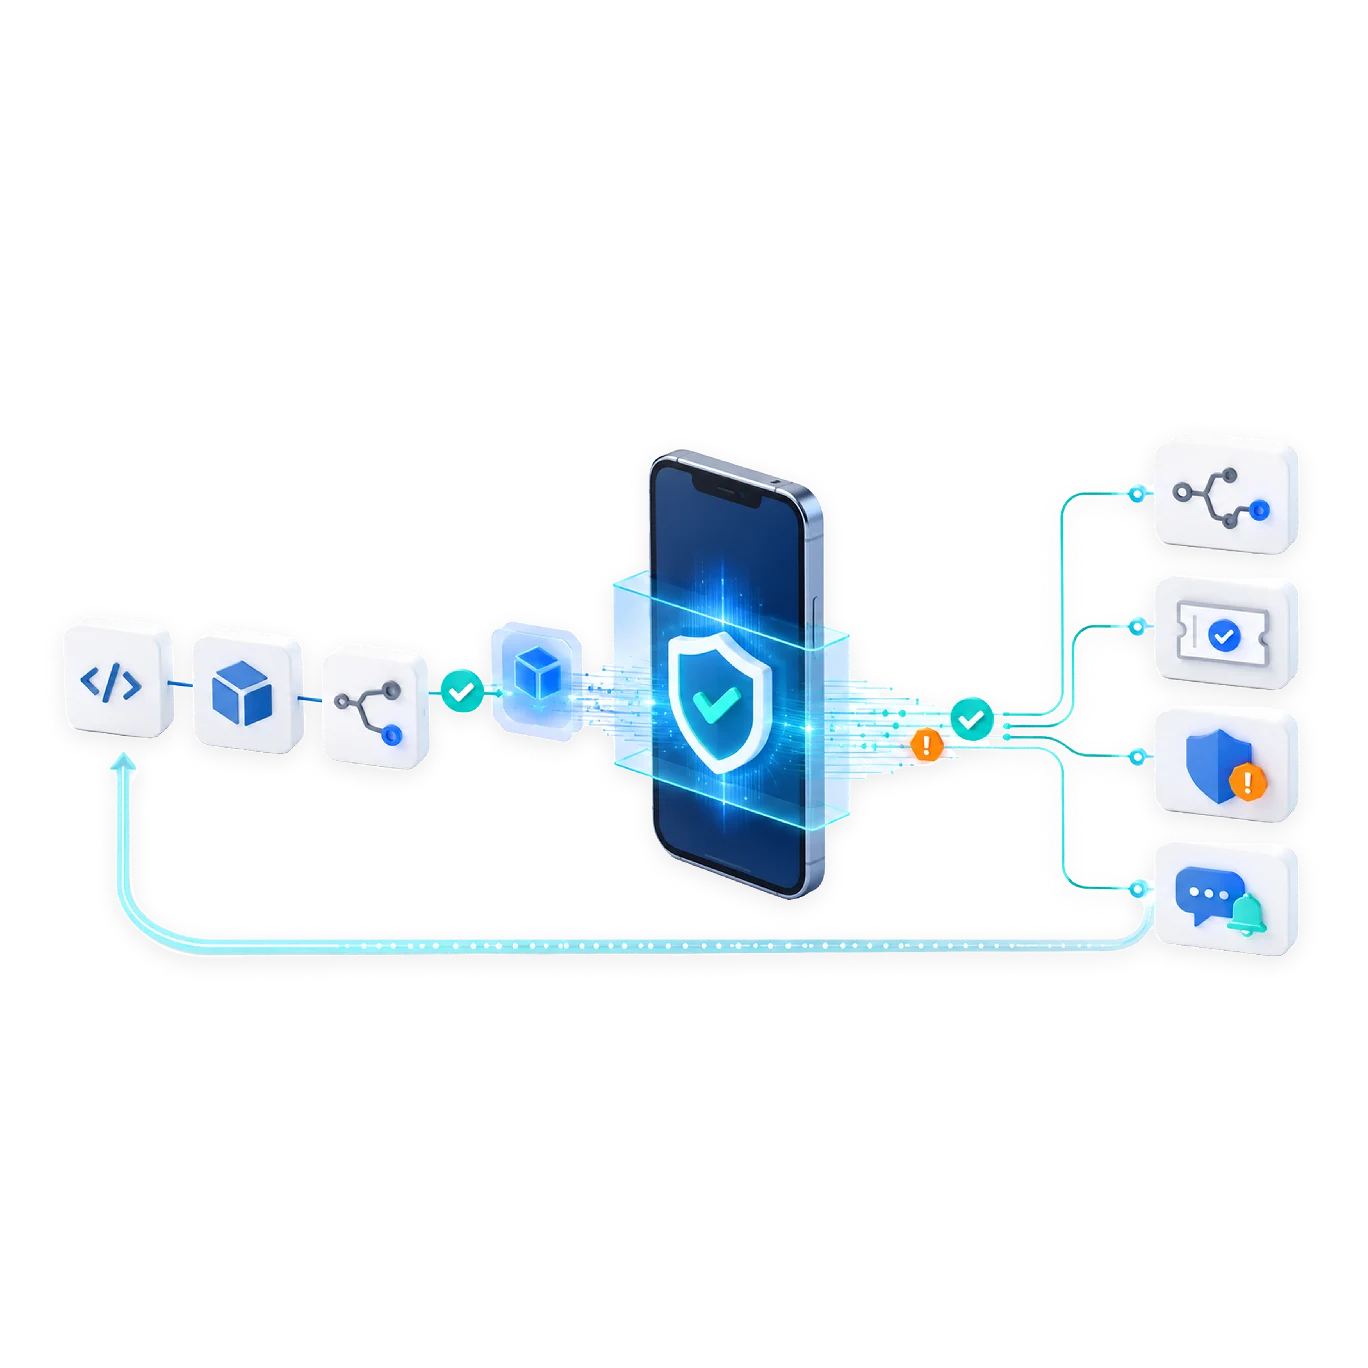
Do away with proprietary files and spreadsheets. No more copy and paste from your reports. NowSecure Platform offers pre-built integrations, open APIs, and native a CLI to power a secure development workflow within existing dev lifecycle processes. Rapidly and securely provide your binaries for testing and consume results in the same workflow with minimal friction.
- GitHub, Microsoft Azure DevOps, Cloudbees Jenkins, CircleCI, GitLab and other CI/CD platforms
- GitHub Issues, Jira, Azure Boards, GitLab Boards and other issue tracking and ticketing systems
- Black Duck CodeDX, Coalfire Threadfix and Brinqa and other vulnerability management systems
- Slack and email alerts
Regulatory Compliance Made Simple
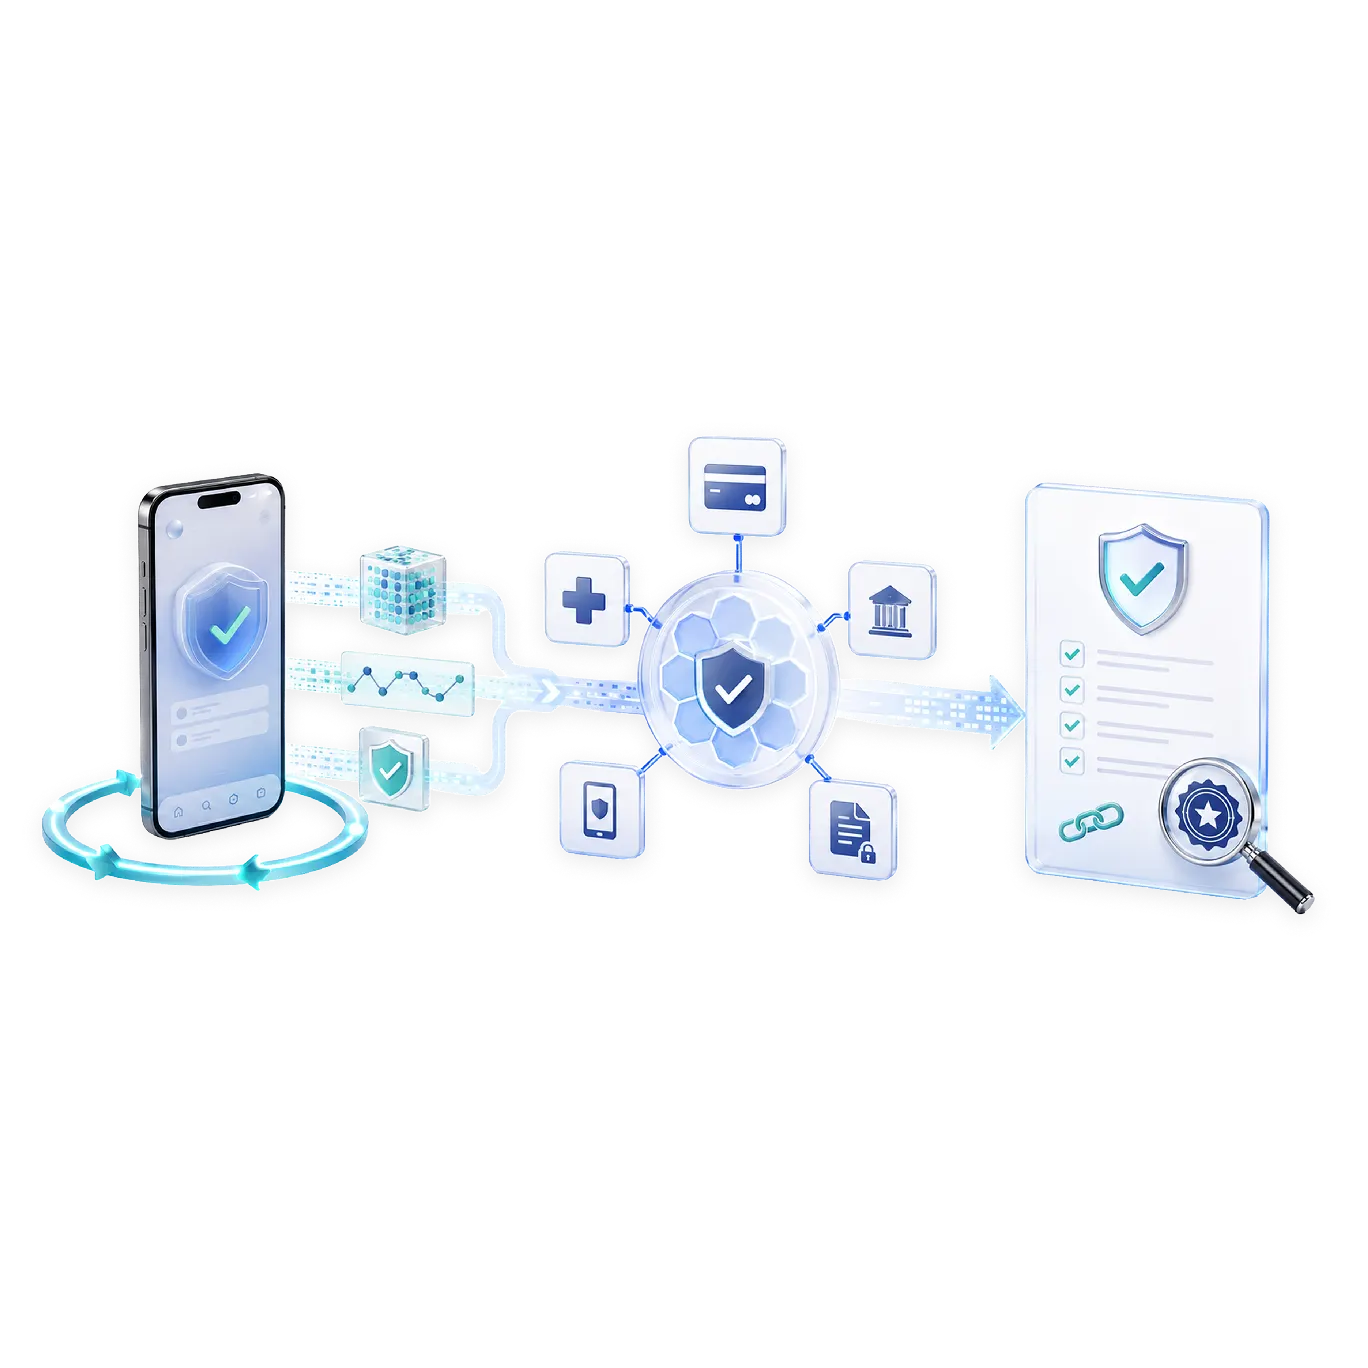
NowSecure PTaaS streamlines regulatory compliance by delivering continuous, audit-
ready app testing aligned with frameworks like OWASP MAS, PCI, HIPAA, NIAP, and more. Continuous testing automates evidence collection, provides clear reporting, always-on compliance validation and supports human-led verification, making it easy to meet compliance requirements without disrupting your development flow.
Goes Beyond iOS and Android
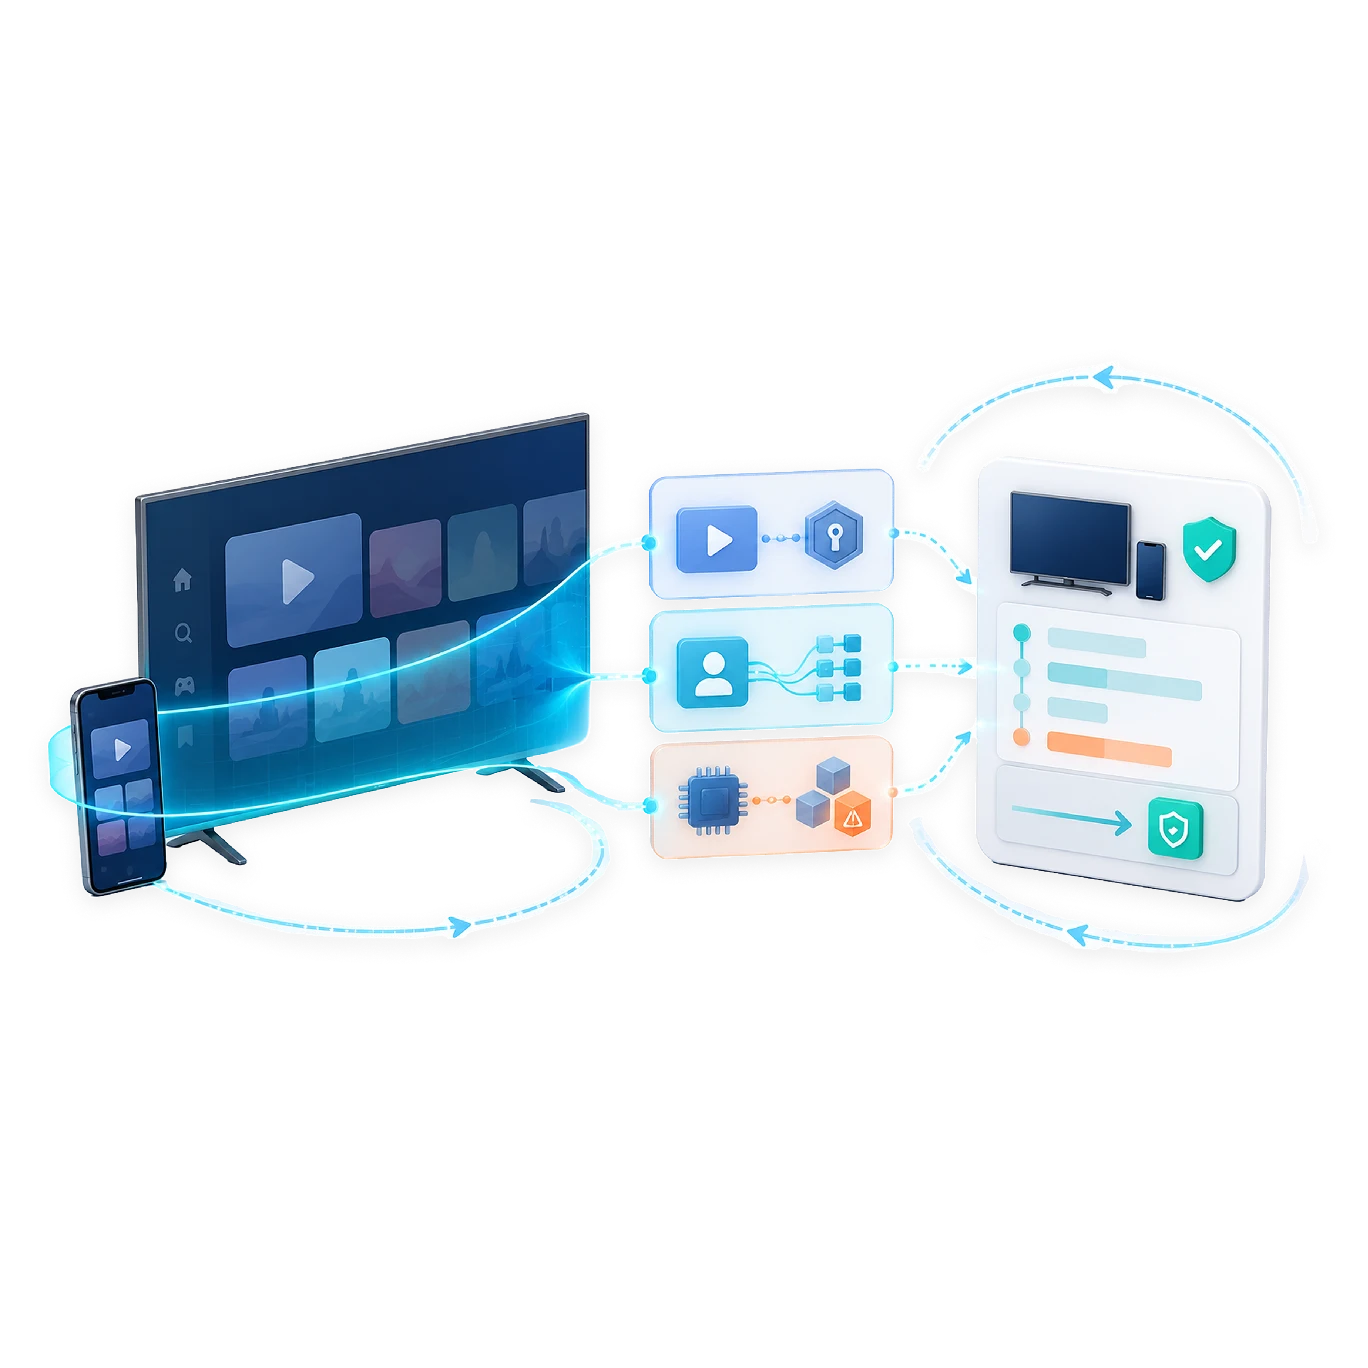
Apps that run on streaming platforms like Roku, Apple TV, and many smart TVs are
called Over-the-Top (OTT) apps. These may contain vulnerabilities or privacy concerns originally overlooked due to the platforms they run on top of. However, these apps are especially interesting to adversaries looking to capitalize on the treasure trove of streaming content and user data these apps handle. With NowSecure PTaaS, organizations can add OTT app testing to their mobile app testing program further mitigating risk all while consolidating these results for ease of access.
Comprehensive Testing
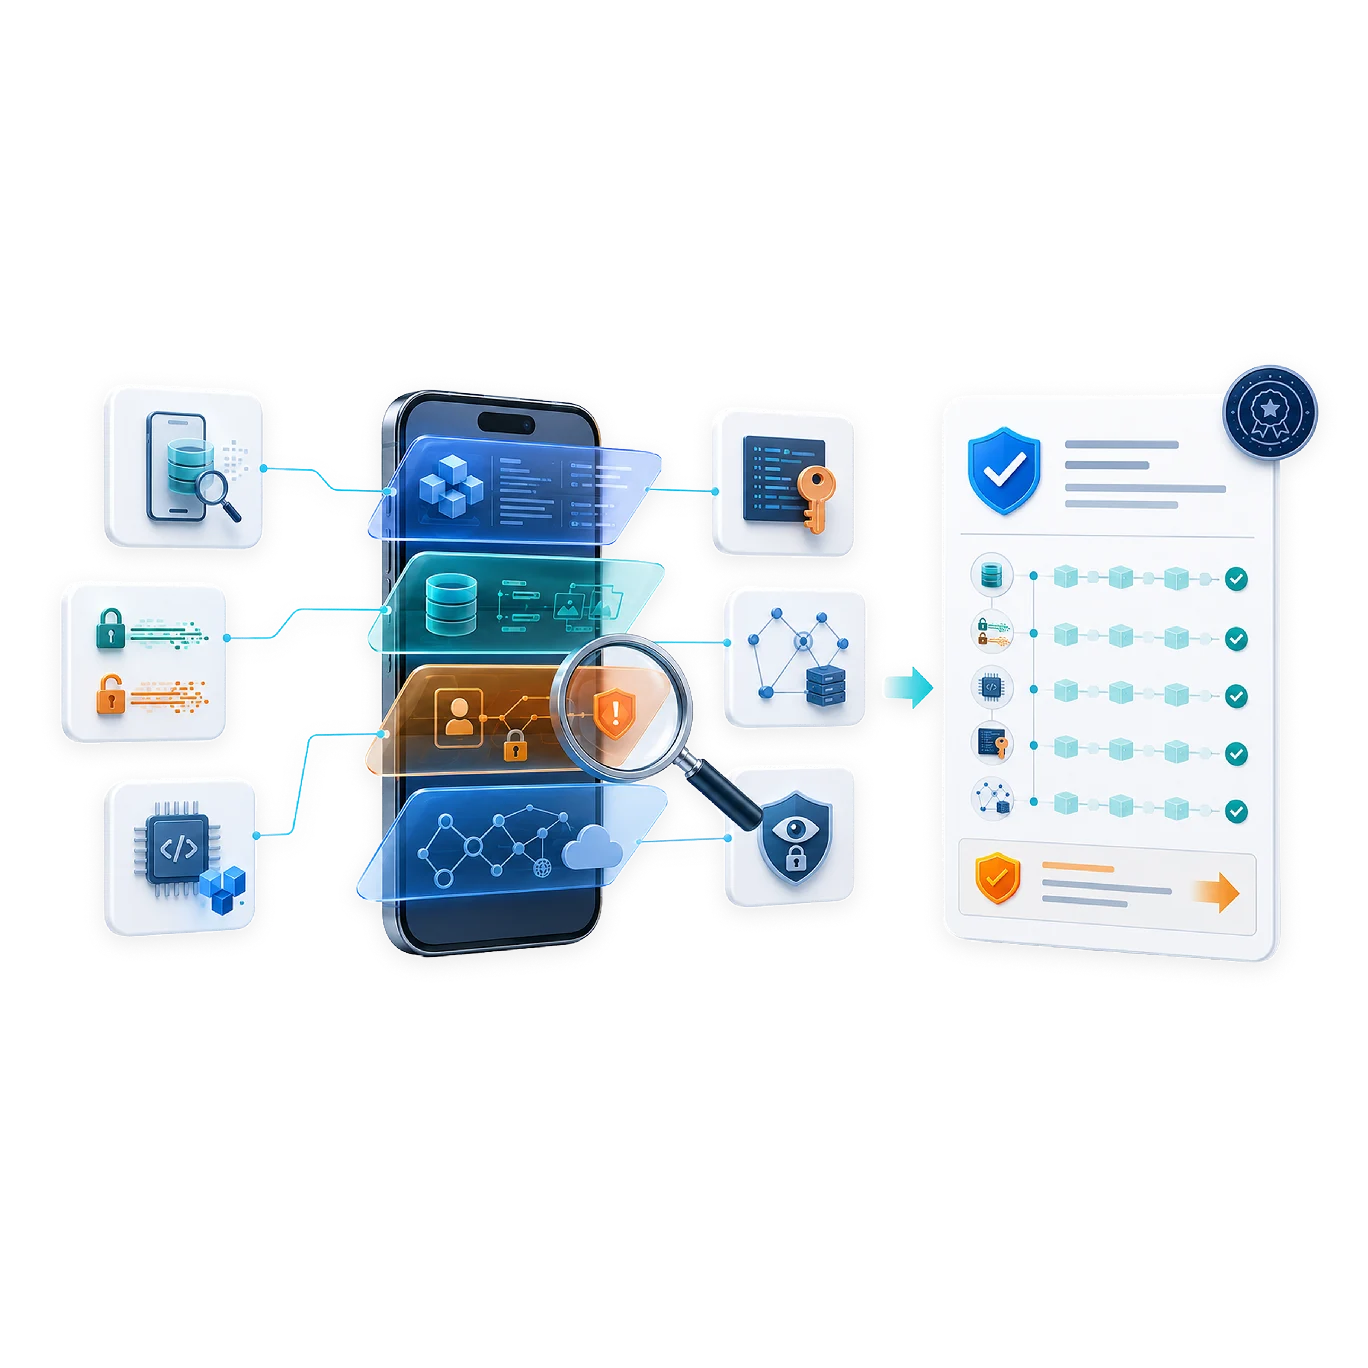
Every assessment is performed by seasoned analysts who rigorously evaluate the full attack surface the app, including client-side code, device interactions, backend APIs, data storage, authentication, and authorization mechanisms. Our testing process adapts to the complexity and risk profile of each app, uncovering vulnerabilities that automated tools often miss, such as business logic flaws, insecure data handling, or nuanced privacy exposures.
- Forensic analysis of data artifacts on the device
- Analysis of network communications, both encrypted and unencrypted
- Analysis of binary resiliency to reverse engineering
- Investigation for hardcoded secrets
- Analysis of API calls
- Privacy exposure
Comprehensive Reporting
and Consultation
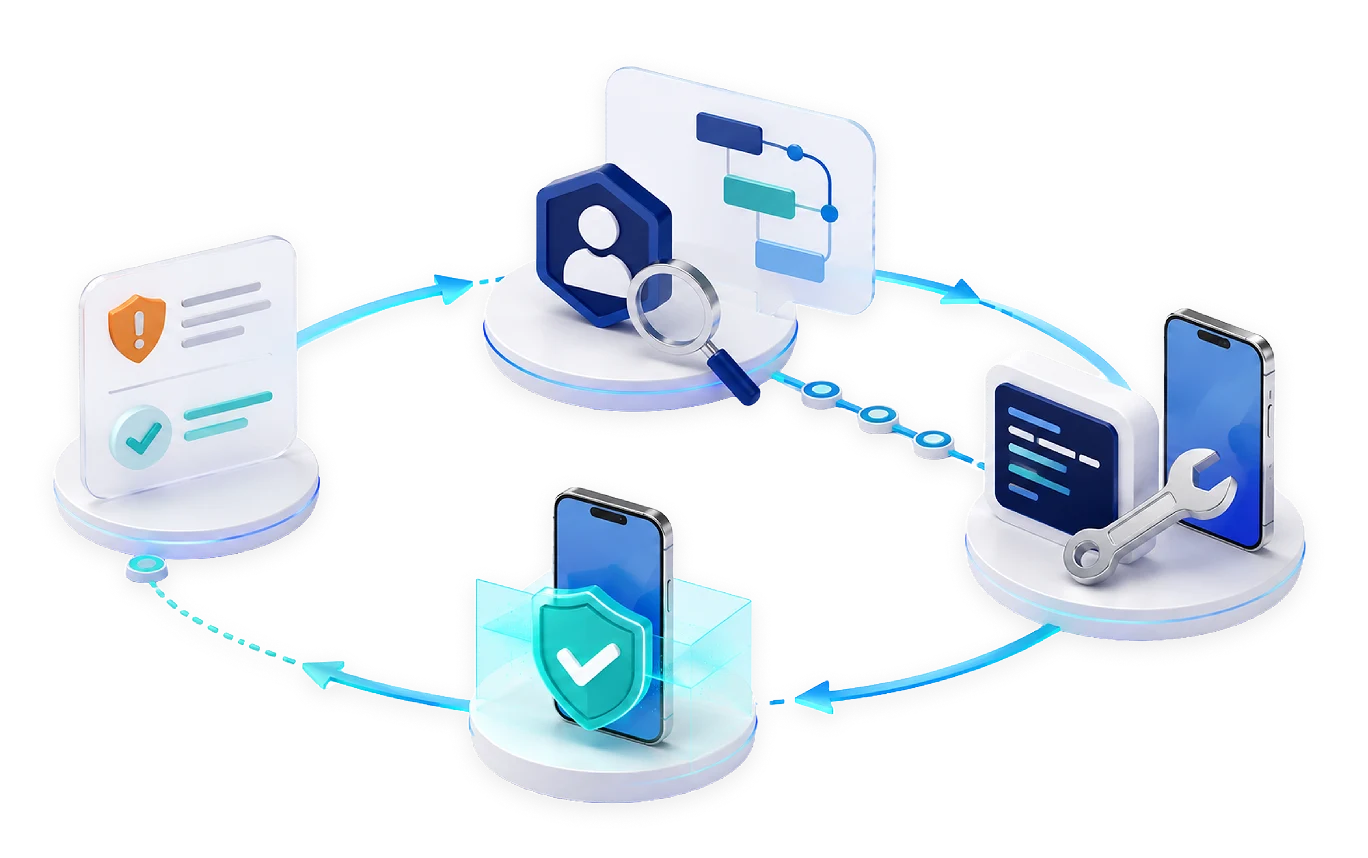
NowSecure PTaaS delivers industry-leading, comprehensive reporting designed to empower developers, security teams, and business stakeholders with clear, actionable insights.
Each report includes:

Detailed vulnerability descriptions with technical context and business impact.

Reproduction steps with technical context and business impact.

Professional remediation guidance tailored to both developers and security practitioners.

References to best practices and industry resources, streamlining knowledge sharing and skill-building.

Mappings to relevant standards and frameworks such as OWASP MASVS, OWASP MASWE, NIAP, PCI DSS, HIPAA, and NIST, supporting regulatory compliance and internal audit requirements.

Threat model context and proof-of-concept (PoC) artifacts, enabling organizations to fully understand exploitation potential and risk exposure.
Consultation That Drives Success
Beyond the report, NowSecure includes free expert consultation as part of every license. Our security analysts conduct thorough report readouts to ensure stakeholders understand findings, remediation paths, and risk implications.
We go further by providing:

Follow-up guidance and support throughout remediation.

Retesting at no additional cost, validating that fixes were implemented correctly and securely.
This combination of deep reporting and human collaboration ensures that your teams are set up for success—both in the short term and across your ongoing security program.
PTaaS Compared to
Traditional Pentesting
How is PTaaS better than Pen Testing?
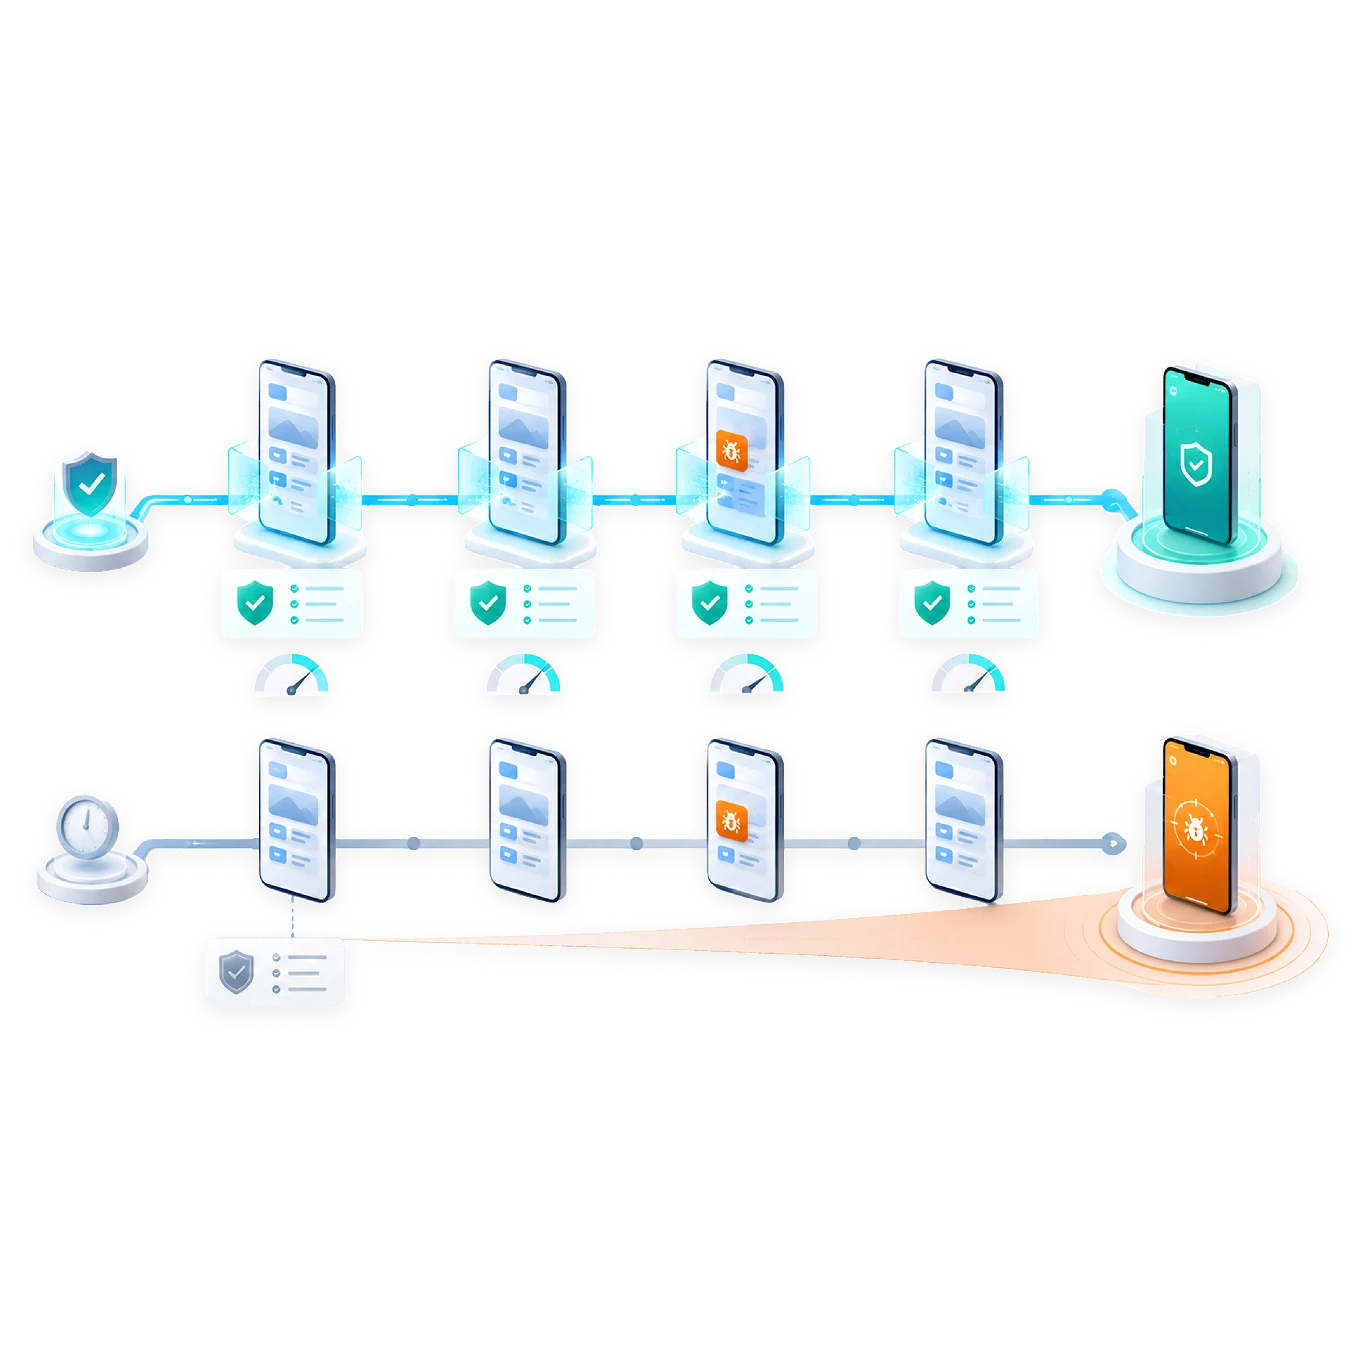
- PTaaS: provides ongoing assessments, enabling detection of new vulnerabilities as code changes, aligning the rigor of testing with the risk and complexity of the application.
- Traditional: pentests are time-bound, often tied to a release or compliance event, leaving long gaps between tests and greater windows of exposure.
Improved Efficiency and Scalability
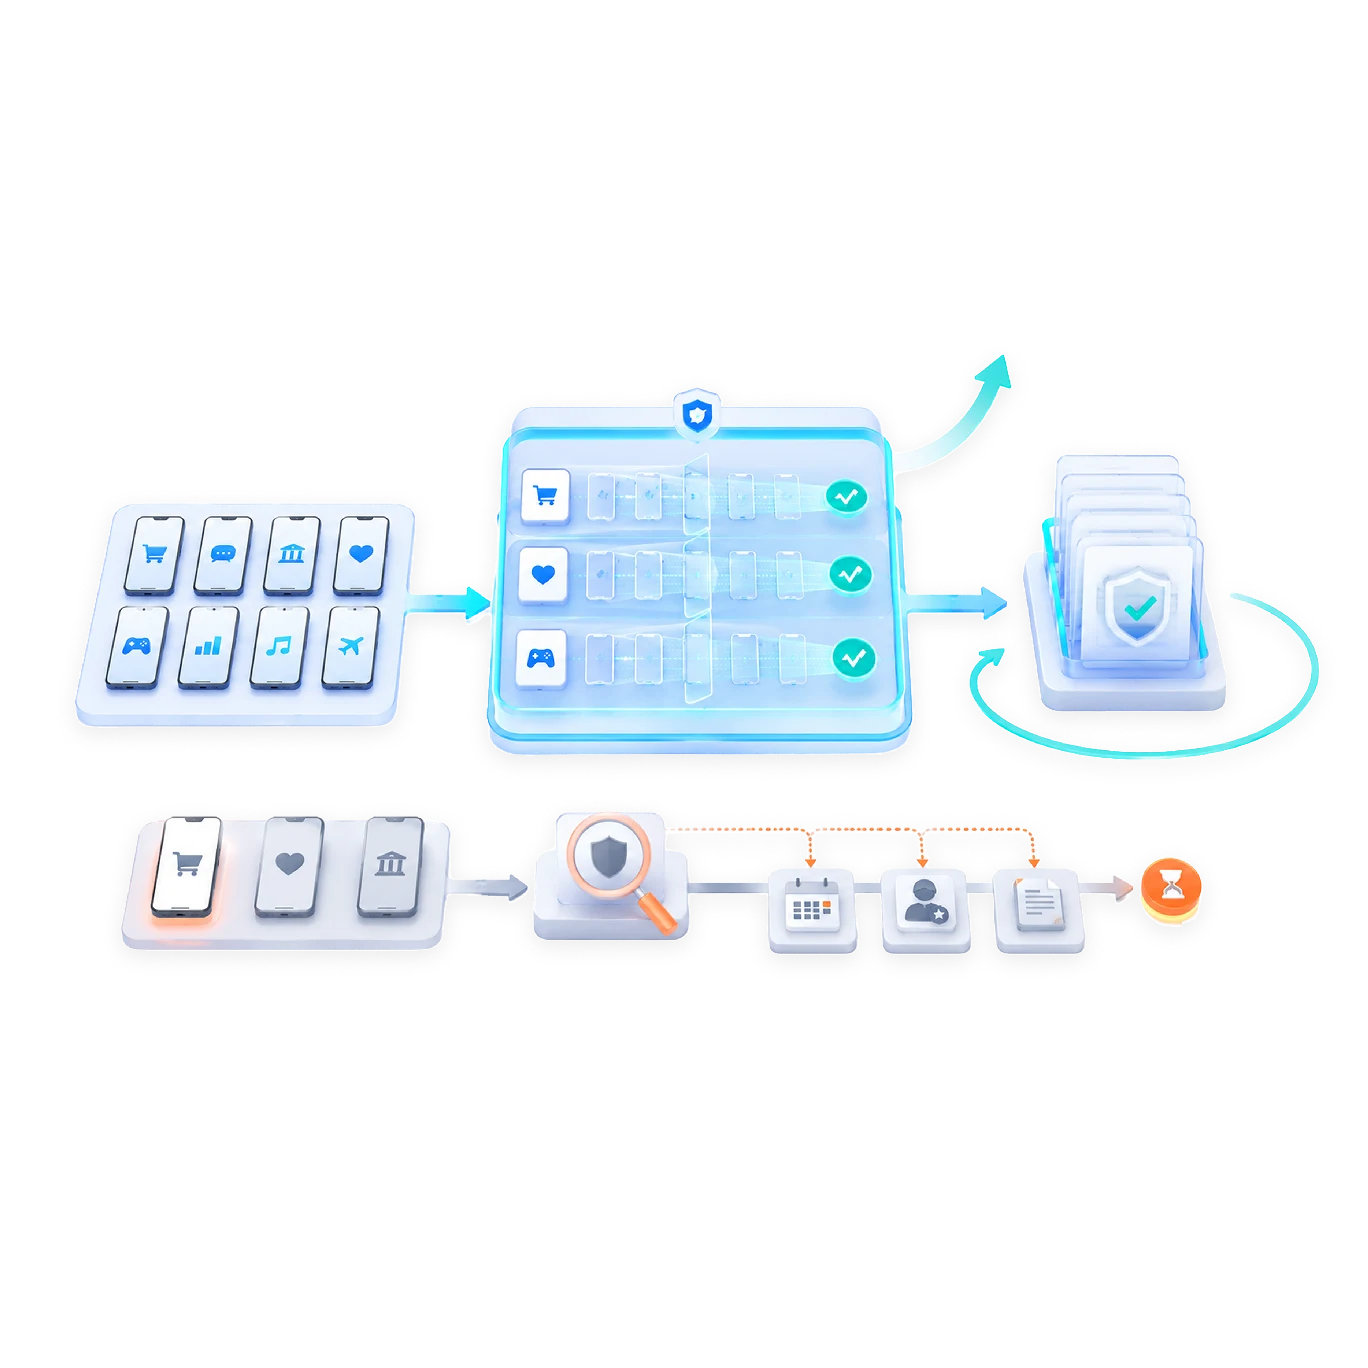
- PTaaS allows organizations to test more frequently and at scale across large app portfolios.
- Traditional methods are manual, costly, and often require separate procurement processes per test, making them hard to scale.
Faster Remediation Cycles
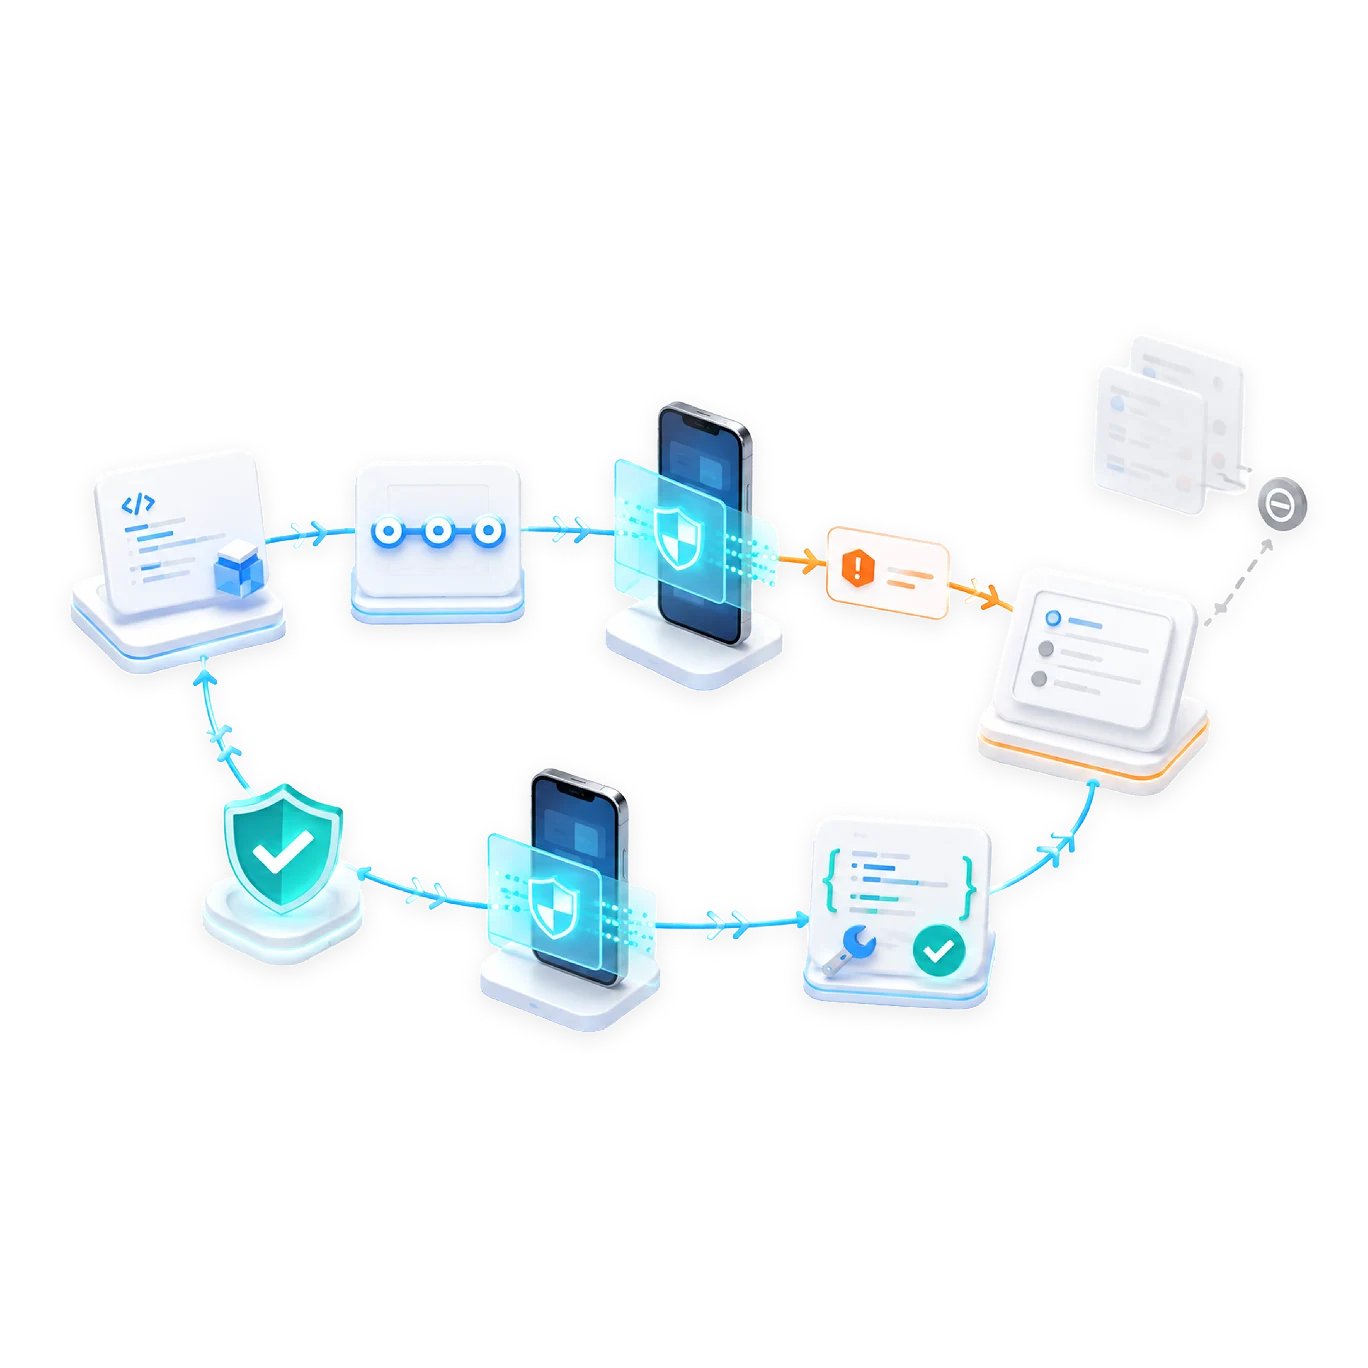
- PTaaS integrates into development pipelines (CI/CD), delivering findings directly into tools like Jira or GitHub.
- This enables rapid remediation, while traditional tests often result in delayed reports that slow down fix timelines.
Hybrid Expertise: Automation + Human Testing
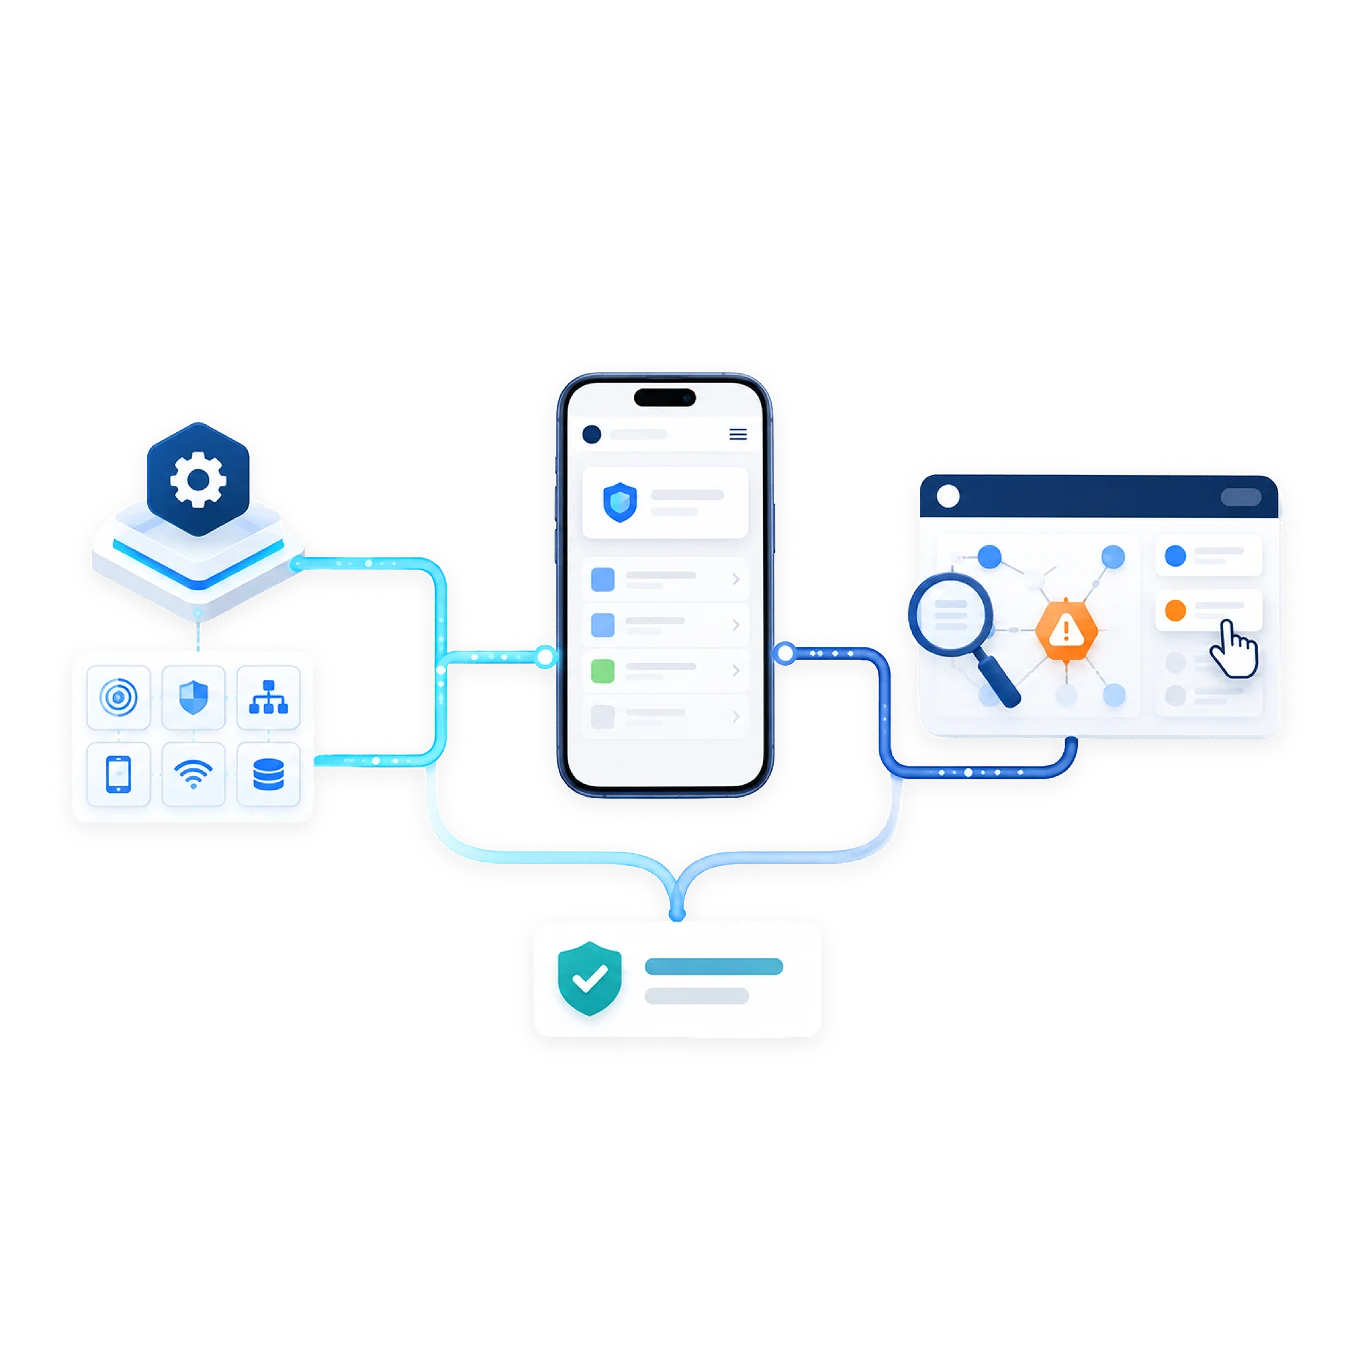
- PTaaS combines automated security testing with expert-led manual assessments, ensuring broad and deep coverage.
- Traditional tests are usually manual-only, limiting frequency and scope due to resource constraints or cost.
Always-On Reporting and Visibility
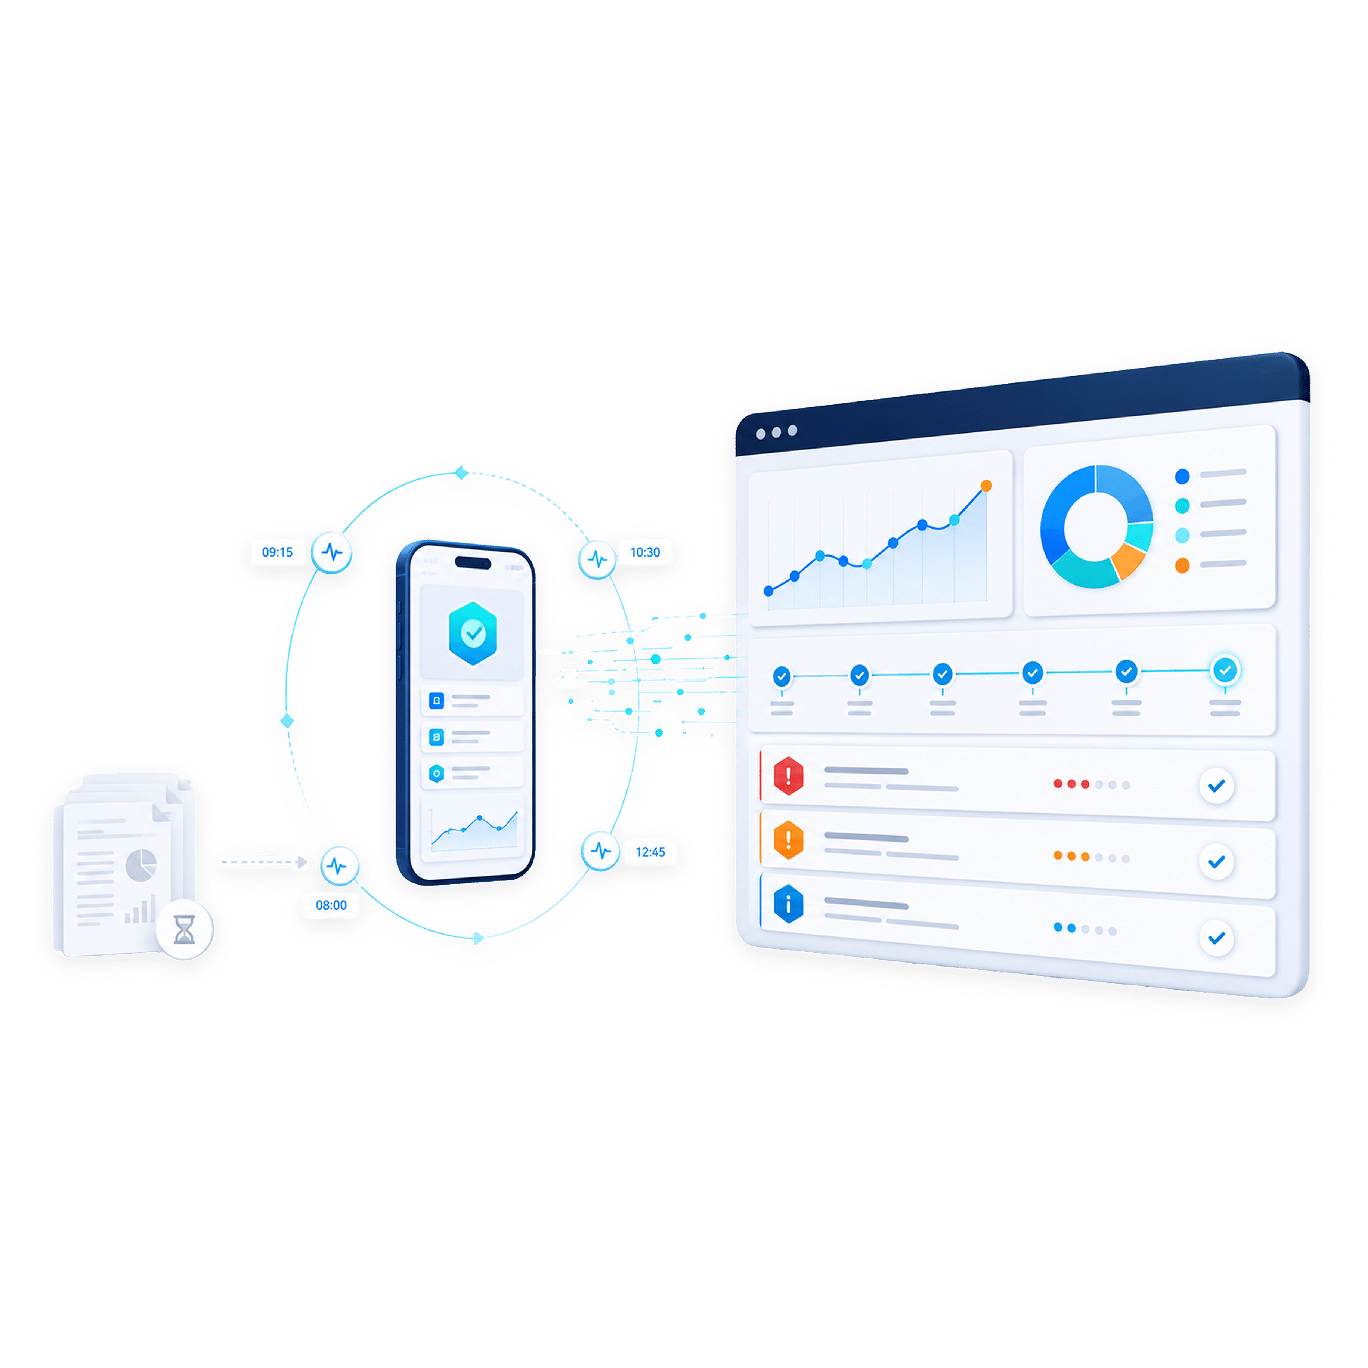
- PTaaS platforms offer real-time dashboards and centralized reports with risk trending, history, and actionable insights.
- Traditional pentesting delivers static PDFs with little to no context, traceability, or integration with development workflows.
Third-party attestation
This combination of deep reporting and human collaboration ensures that your teams are set up for success—both in the short term and across your ongoing security program.
At the conclusion of each assessment, organizations can request a NowSecure- issued attestation letter that confirms:
These signed attestations serve as trusted documentation for internal auditors, partners, regulators, and customers, and are particularly useful during compliance reviews, vendor risk assessments, and procurement processes.


Request a Mobile
PTaaS Consultation
Experience the NowSecure Difference
Resources
PTaaS resources
Frequently asked questions about
penetration testing
Have more questions? Get in touch with our team.