
Research & Threat Intel
On Oct. 25, 2022, OpenSSL began pre-notifying organizations of two critical vulnerabilities in OpenSSL 3.0.x. On the positive side, OpenSSL 3.0 had not been widely deployed yet, and even better on Nov 1, 2022, the two vulnerabilities were downgraded from critical to high. However, on the heels of other recent highly impactful vulnerabilities like Log4j […]
NowSecure recently partnered with Coalfire to contribute mobile risk data to the cybersecurity advisory company’s 4th Annual Penetration Risk Report. The report findings reveal the importance of continuous testing in vulnerability management combined with human-based testing to reduce risk. The most successful vulnerability and risk management programs are no longer focused on point-in-time schedules but […]
TL;DR: The Peloton Bike ran an unpatched version of Android 7 which led to it being vulnerable to a number of known issues, most significantly CVE-2021-0326, which could allow an attacker within WiFi range to execute arbitrary code on the device. There is no requirement for the user to interact with any attacker controlled data, […]
Escalating software supply-chain attacks pose a serious threat to the public sector and organizationes. Adversaries exploit vulnerabilities in third-party code to compromise a supplier to the vast digital ecosystem downstream. The ripple effect causes widespread disruption, financial loss and reputational damage and even endangers national security. Consider the enormous impact the SolarWinds software supply chain […]
Peloton has become perhaps the most well known and successful fitness equipment company today. It makes several connected fitness products including popular Internet-connected stationary exercise bikes and publishes an impressive library of live and on-demand course content. The class platform offers an immersive experience that makes exercise fun and competitive. But this blog post isn’t […]
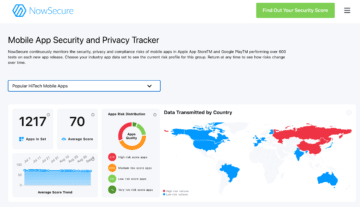
Tapping the power of NowSecure Platform, the NowSecure MobileRiskTracker™ interactive benchmark portal continuously scans millions of mobile apps from public app stores. The tool aggregates this data anonymously to show real-time security and privacy analysis of the most popular mobile apps in 12 industry categories.
So how loaded for Bear should mobile app developers and mobile app users be? Where and why are nation-state actors targeting mobile vulnerabilities?
In response to high-profile cyberattacks, the U.S. White House announced stringent new cybersecurity guidelines to strengthen American cyberdefenses. Set to roll out over the next year, federal agencies, their private-sector partners and software vendors must begin to prepare their software and services to comply, including mobile apps. Released on May 12, 2021, the Executive Order […]
Picture a world where you browse the web without that little lock next to the URL to assure that your web communications are safe, well at least for the most part anyway. That’s the current state of security with Bluetooth Low Energy (BLE), and more generally the Internet of Things (IoT.) I propose a system to solve the BLE authentication puzzle by automating, and hopefully standardizing, IoT security testing.