MOBILE Application SECURITY TESTING (MAST)
Mobile app security testing for the app your users actually install
Source-code scanners test what your developers wrote. NowSecure tests the compiled iOS and Android app on real devices, logged in, with every SDK and AI feature inside it, then hands developers findings backed by runtime evidence.
TRUSTED BY ENTERPRISE TEAMS THAT BUILD, SECURE, AND GOVERN MOBILE APPS
WHY MOBILE IS DIFFERENT
What is mobile app security testing?
Mobile app security testing (MAST) is the process of finding security and privacy flaws in iOS and Android apps. It analyzes the compiled app binary, runs the app on a device to see how it stores data, handles logins, and talks to APIs, and inspects the third-party SDKs bundled inside it. OWASP MASVS defines the requirements a secure mobile app should meet, and the OWASP MASTG defines how to test against them.
MAST is its own category because mobile apps run on devices you do not control. Anyone can download your app, decompile it, attach a debugger, and watch its traffic. Testing that stops at the source code or at the API layer misses most of what that person would find.
WHAT MAST FINDS
What mobile app security testing finds that source-code scanning misses
Testing behind the login is where most of the difference shows up. NowSecure research found that authenticated mobile app security testing finds 78% more sensitive data risk.
| Where the risk lives | What goes wrong | How NowSecure tests it |
|---|---|---|
| The compiled binary | Hardcoded API keys and tokens, embedded endpoints, weak build settings | Static and binary analysis of the IPA or APK you ship, not the repository |
| Local storage on the device | Session tokens or personal data written to logs, caches, or unprotected storage | Dynamic analysis on real iOS and Android devices |
| Behind the login | Session handling, token refresh, and account data flows that unauthenticated scans never reach | AI-Navigator completes the login so dynamic testing reaches post-login screens |
| Network and APIs | Weak TLS, bypassable certificate pinning, sensitive data sent to the wrong endpoint | Traffic captured through the authenticated session, from the app's side |
| Third-party SDKs | Analytics, advertising, and payment SDKs collecting or sending data your team never approved | Runtime SDK and dependency analysis, plus a dynamic mobile SBOM |
| AI features | Prompts, user data, or model traffic sent to third-party AI services | AI detection that identifies AI SDKs, models, and the data flowing to them |
HOW MAST COMPARES
MAST vs. SAST, DAST, and penetration testing
Most mobile programs need MAST on every build and mobile app penetration testing on the releases that carry the most risk.
| Approach | What it tests | Where it falls short for mobile | Where it fits |
|---|---|---|---|
| SAST | Source code in the repository | Never sees the compiled app, bundled SDKs, or runtime behavior | Code-level checks in pull requests |
| Web DAST | A running web app or API, from the outside | Cannot run a mobile app, bypass pinning, or inspect on-device storage | Backend and API testing |
| MAST | The compiled mobile app, both statically and running on a device | Automation does not replace a human tester for novel business logic abuse | Every build, in CI/CD |
| Mobile pen testing | The app, attacked by a skilled human tester | Too slow and costly to run on every build | Major releases, high-risk apps, and compliance |
FROM BUILD TO FIX
How NowSecure mobile app security testing works
The NowSecure Platform takes every build from upload to fix in five steps.
| Step | What happens |
|---|---|
| 1. Connect a build | Upload an IPA or APK, or trigger tests automatically from GitHub Actions, GitLab, Azure DevOps, Jenkins, CircleCI, or Bitrise. |
| 2. Analyze the binary | Static and binary analysis maps the app's code, libraries, SDKs, and embedded secrets. |
| 3. Run it on real devices | Dynamic analysis exercises the app on physical iOS and Android hardware, logs in with AI-Navigator, and captures runtime behavior and network traffic. |
| 4. Correlate and report | Findings are mapped to OWASP MASVS, checked against both static and dynamic evidence, and sent to your tracker with remediation guidance. |
| 5. Go deeper where it matters | Add Guided Testing or pen testing as a service when an app needs an analyst to work through MFA, CAPTCHA, or complex business logic. |
EVIDENCE WITH EVERY FINDING
Findings your developers will act on
A security tool that floods the backlog gets switched off. Every NowSecure finding ships with the evidence that produced it: the file in the binary, the runtime behavior, or the captured request. It also includes the MASVS requirement it maps to and a fix your developers can apply. Teams set risk-based release policies, so only findings above their threshold block a build.
Tickets include remediation suggestions from NowSecure which are very, very helpful.
Micha Katz, Chief Information Security Officer, Yellow Card
See what NowSecure finds in your app
Bring one of your iOS or Android apps to a demo. We'll show you what turns up in the binary, on a real device, and behind the login.
DevSecOps Integration
Mobile app security testing in your DevSecOps pipeline
Mobile apps change with every release: new features, updated SDKs, new AI services. NowSecure runs in the pipeline you already use, so every build is tested before it ships.
What gets retested on every build:

New application builds

Updated functionality

Changed security controls

Third-party SDK updates

Application behavior changes
Where testing runs in your lifecycle:
Software Supply Chain
Third-party SDK and software supply chain testing
Analytics, advertising, payment, and AI SDKs become part of the app you ship, running with the same access to user data as your own code. NowSecure identifies every component inside the compiled app and watches what each one does at runtime.
What SDK analysis shows you:
Which SDKs and libraries are inside your app
Which components have known vulnerabilities
What app data and device capabilities each SDK can access
Where SDKs send data outside your app
Get a full inventory of every component in your app with a dynamic mobile SBOM.
Emerging Risk
AI-Powered Mobile Application Security Testing
Artificial intelligence is changing how mobile applications are designed, developed, and delivered. AI-powered features can improve user experiences and accelerate innovation, but they also introduce new application behaviors, data flows, and dependencies that require specialized security testing.
Mobile applications increasingly incorporate AI capabilities, third-party AI services, and intelligent features that interact with sensitive data and application functionality. Mobile App Security Testing helps teams evaluate how AI-enabled functionality impacts the security of the application and the data it processes.
How Does AI Change Mobile Application Security?
AI introduces new application behaviors and data flows that can expand the mobile attack surface.
AI-enabled mobile applications may introduce risks related to:
Sensitive data access and exposure
New communication paths between applications and AI services
Third-party AI components and dependencies
Changes in application behavior introduced through AI functionality
Security controls around AI-enabled features

As AI becomes more embedded in mobile experiences, security teams need visibility into how these capabilities affect application security.
How Does MAST Evaluate AI-Enabled Applications?
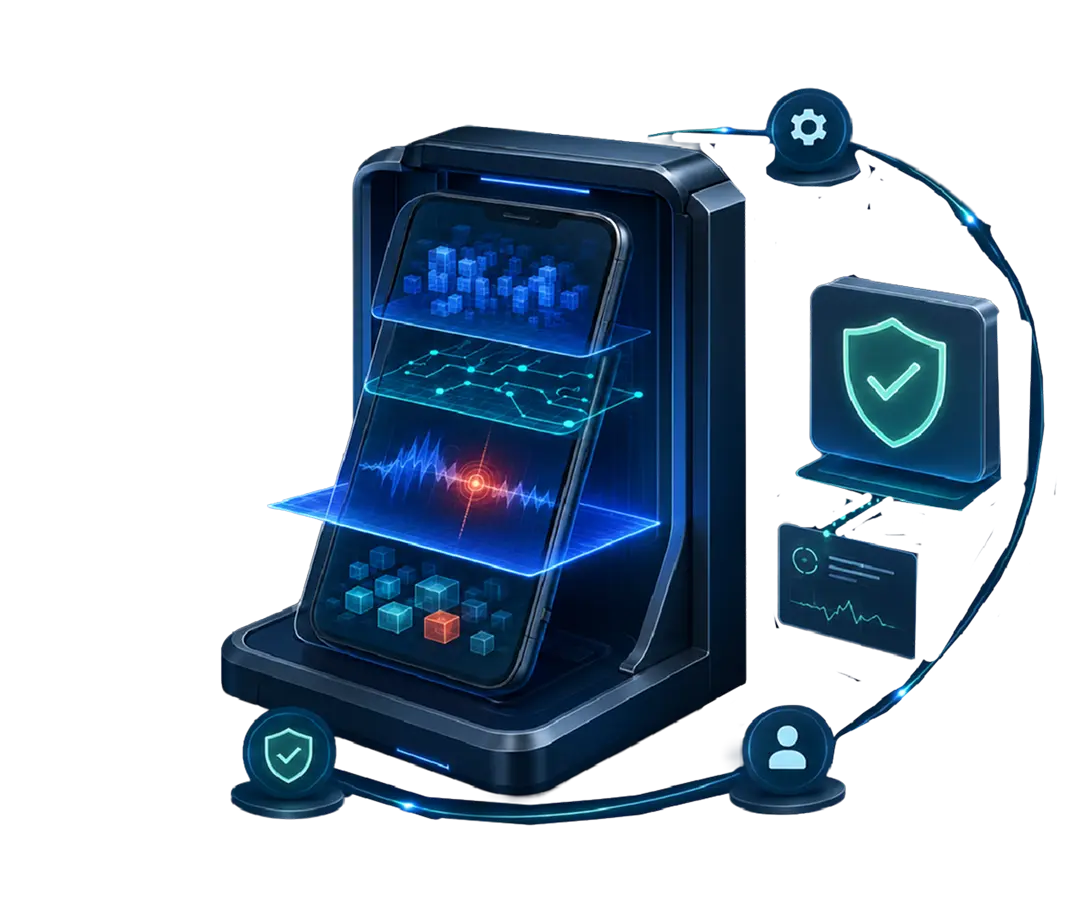
Mobile App Security Testing helps teams assess AI-powered applications by analyzing the application environment, including:
By evaluating AI-powered applications as part of the complete mobile security testing process, teams can identify emerging risks while continuing to deliver innovative mobile experiences.
How Does MAST Evaluate AI-Enabled Applications?
| Category | Includes |
|---|---|
| Application Surface | Mobile Application, AI Features, Data Access, Third-Party AI Services, APIs, User Interactions |
| Security Testing Focus | Behavior Analysis, Data Flow Analysis, Component Analysis, Risk Identification |
Open standards, open source
Open standards, open source
NowSecure helps write the OWASP mobile standards it tests against. Carlos Holguera, a NowSecure principal research engineer, co-leads the OWASP Mobile Application Security project that maintains MASVS and MASTG.
| Standard or credential | What it is | NowSecure's role |
|---|---|---|
| OWASP MASVS | The security requirements a mobile app should meet | Tests against it and co-leads the OWASP project that maintains it |
| OWASP MASTG | The methodology for testing apps against MASVS | Follows it in every assessment |
| Frida and radare2 | Open source instrumentation and reverse engineering tools widely used by mobile security testers | Supports both projects: Frida and radare2 |
| ISO/IEC 17025:2017 | The international accreditation standard for testing laboratories | A2LA-accredited lab (Cert. No. 7003.01) for MASA and MASVS Level 1 |
See how each MASVS domain is covered in the OWASP mobile app security testing overview and on the mobile standards and compliance page.
The NowSecure Difference
Why Choose NowSecure for Mobile App Security Testing?
Mobile security requires specialized expertise. NowSecure was built specifically for mobile application security, combining automated analysis, expert testing, and deep mobile research to help organizations identify and validate security risks across iOS and Android applications.
| Differentiator | Description |
|---|---|
| Purpose-Built Mobile Security Expertise | Unlike general application security platforms, NowSecure focuses specifically on mobile applications and the unique risks introduced by mobile binaries, APIs, runtime behavior and third-party components. |
| Proven Mobile Security Research and Intelligence | NowSecure’s expertise is informed by millions of mobile application assessments, ongoing security research and contributions to the broader mobile security community. |
| Industry and Open-Source Leadership | NowSecure contributes to mobile security standards and open-source projects that advance mobile application analysis and security testing, including OWASP Mobile Security standards, Frida and radare2. |
| Comprehensive Mobile Security Testing | NowSecure combines automated testing, expert analysis and mobile-specific expertise to evaluate evolving mobile application risks, including new security considerations introduced by AI-enabled applications. |
See and govern the AI inside your mobile apps
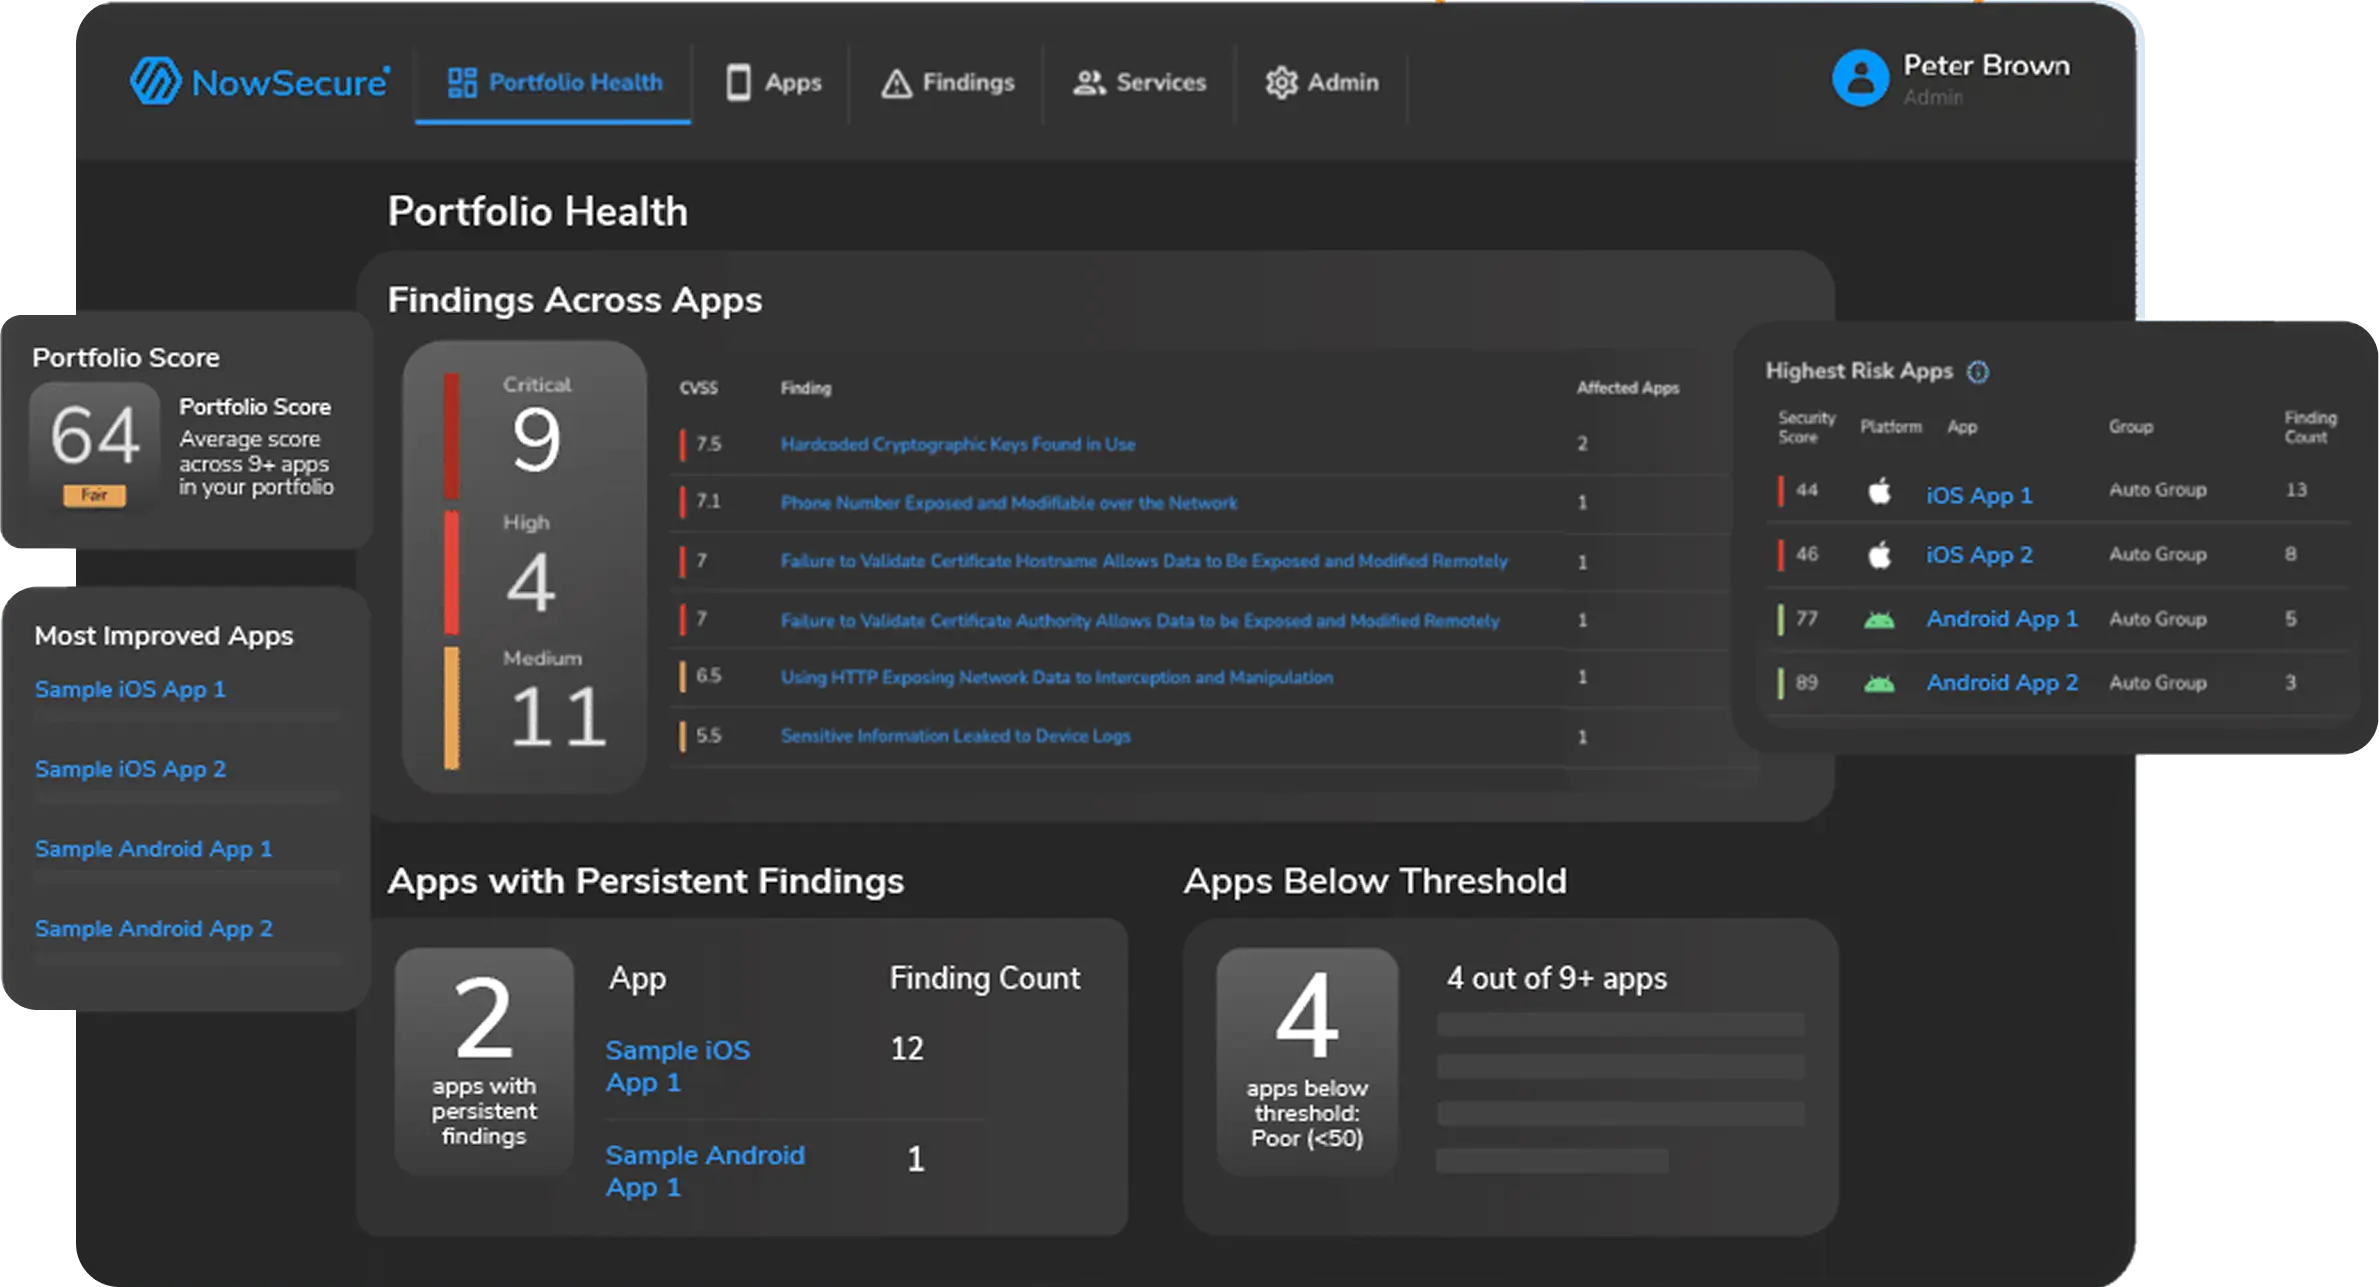
Get a clear view of the AI, SDKs, generated code, and data flows inside your apps, plus prioritized guidance your teams can use to reduce risk and move faster.
Resources
Mobile Application Risk Management Resources