Mobile App Pen Testing Services
Mobile app penetration testing that gets past the login screen
Most mobile testing stops at the login screen, which is where the real attack surface starts. NowSecure pen testers work on real iOS and Android hardware, inside the authenticated session, where the tokens,
the API traffic, and the customer data actually live.

Beyond conventional scanning
What most mobile pen tests miss
A mobile app's real attack surface sits behind authentication and inside the compiled binary sitting on the device. Source-code scanning and emulator testing cannot reach either one. They miss how the app stores a session token in the keychain, how it behaves when certificate pinning is bypassed, what its third-party SDKs transmit after login, and what someone with a rooted handset can pull out of it.
NowSecure runs authenticated dynamic analysis on real physical iOS and Android devices, paired with binary analysis of the artifact you actually ship. A finding has to show up in both before it reaches your developers.

Risks That Only Appear on Real Devices
Real devices expose certificate pinning, compromised-device and secure-storage risks that emulators miss. NowSecure pen testing uses checkm8, palera1n, and Dopamine toolchains on the relevant iOS generations, and Objection on Android.

Vulnerabilities Hidden Behind Login
AI-powered testing reaches beyond login, with experts handling MFA, CAPTCHA and complex flows.

Findings Without Complete Validation
Every finding is validated across the app binary (apktool, jadx, Ghidra, radare2) and authenticated runtime, reducing false positives before it reaches developers.
Actionable by design
What lands in your developers' queue
A pen test only pays for itself if the findings get fixed. Every engagement includes:

A threat model for this specific app
Sensitive data, critical IP, dependent infrastructure, and the attack paths that actually matter for it, not a generic checklist.

Findings mapped to OWASP MASVS domains
Findings mapped with the runtime and binary evidence that produced each one attached.

Remediation guidance written for developers
The attacker path, the exploitability, and the code change, explained by the analyst who found it.

A targeted retest
A retest to confirm the fix before the release ships.

Compliance evidence generated every assessment cycle
Evidence rather than at point-in-time audit intervals, covering SOC 2, GDPR, CCPA, COPPA, and HIPAA reporting needs. Compliance determination stays with your legal and compliance counsel.
Evidence by technique
How each testing technique maps to
MASVS domains
Authenticated dynamic analysis produces primary evidence for five of the eight OWASP MASVS v2 domains. Static and binary analysis covers the other three. MASTG drives the methodology.
| MASVS domain | Authenticated dynamic analysis Real physical device, after login | Static and binary analysis apktool, jadx, Ghidra, r2 |
|---|---|---|
| Storage Local data at rest | Primary evidence | Augmenting evidence |
| Crypto Cryptography use | Augmenting evidence | Primary evidence |
| Auth Authentication and session | Primary evidence | Not a primary lane for this domain |
| Network Transport and API traffic | Primary evidence | Not a primary lane for this domain |
| Platform Platform interaction and IPC | Augmenting evidence | Primary evidence |
| Resilience Anti-tamper and reverse-engineering defense | Primary evidence | Augmenting evidence |
| Code Code quality and build settings | Not a primary lane for this domain | Primary evidence |
| Privacy Data collection and sharing | Primary evidence | Augmenting evidence |


- Primary evidence
- Augmenting evidence
- Not a primary lane for this domain
Domain names are the OWASP MASVS categories. Each mark shows the technique that exercises the domain.
Scale Mobile App Penetration Testing by Risk
Get the depth each app actually needs
Not every app in your portfolio warrants the same test. Tier them by risk, then match the engagement to the tier. That is how teams keep pen testing spend proportional to exposure.

Continuous testing with Mobile PTaaS
Platform automated testing runs with every build in your CI/CD pipeline, routes findings into developer workflows and adds scheduled expert assessments for fast-moving apps.
Platform Guided Testing
Expert-led testing on real devices examines complex user journeys across attacker-controlled network conditions.
Full-scope and focused pen tests
Scoped expert testing of the full app or critical workflows for independent third-party verification, validation, compliance evidence or added team capacity.
Pen Testing Led by Mobile Security Experts
Expert-Led Mobile App Penetration Testing
NowSecure engineers build the tools other mobile pen testers use. Frida, the dynamic instrumentation framework, and radare2, the reverse engineering toolkit, are both open source projects NowSecure supports and contributes to. Carlos Holguera, a NowSecure principal research engineer, co-leads the OWASP Mobile Application Security project, which produces the MASVS standard and the MASTG methodology this test follows.
A2LA ISO/IEC 17025:2017 accredited laboratory.
Cert. No. 7003.01. Accredited scope covers MASA and OWASP MASVS Level 1, which is narrower than the full binary and dynamic depth a NowSecure pen test applies.

Extend your platform, don't replace it
An Independent Security Review from an authorized lab is what lets you populate the Google Play Data safety section with a verified assessment rather than a self-declaration.

NIAP.
Testing against the Application Software Protection Profile v2.0, the evaluation requirement federal agencies apply to the mobile apps they build and use.
Flexible by risk tier
When a mobile app needs a pen test
Not every app in your portfolio warrants the same test. Tier them by risk, then match the engagement to the tier. That is how teams keep pen testing spend proportional to exposure.
Trusted Mobile App Penetration Testing for Leading Teams
See how leading teams secure their mobile apps


Bring us your
highest-risk app
Send one app and the scope you have in mind. A NowSecure pen tester will walk the threat model with you and tell you what depth it warrants before you commit to anything.
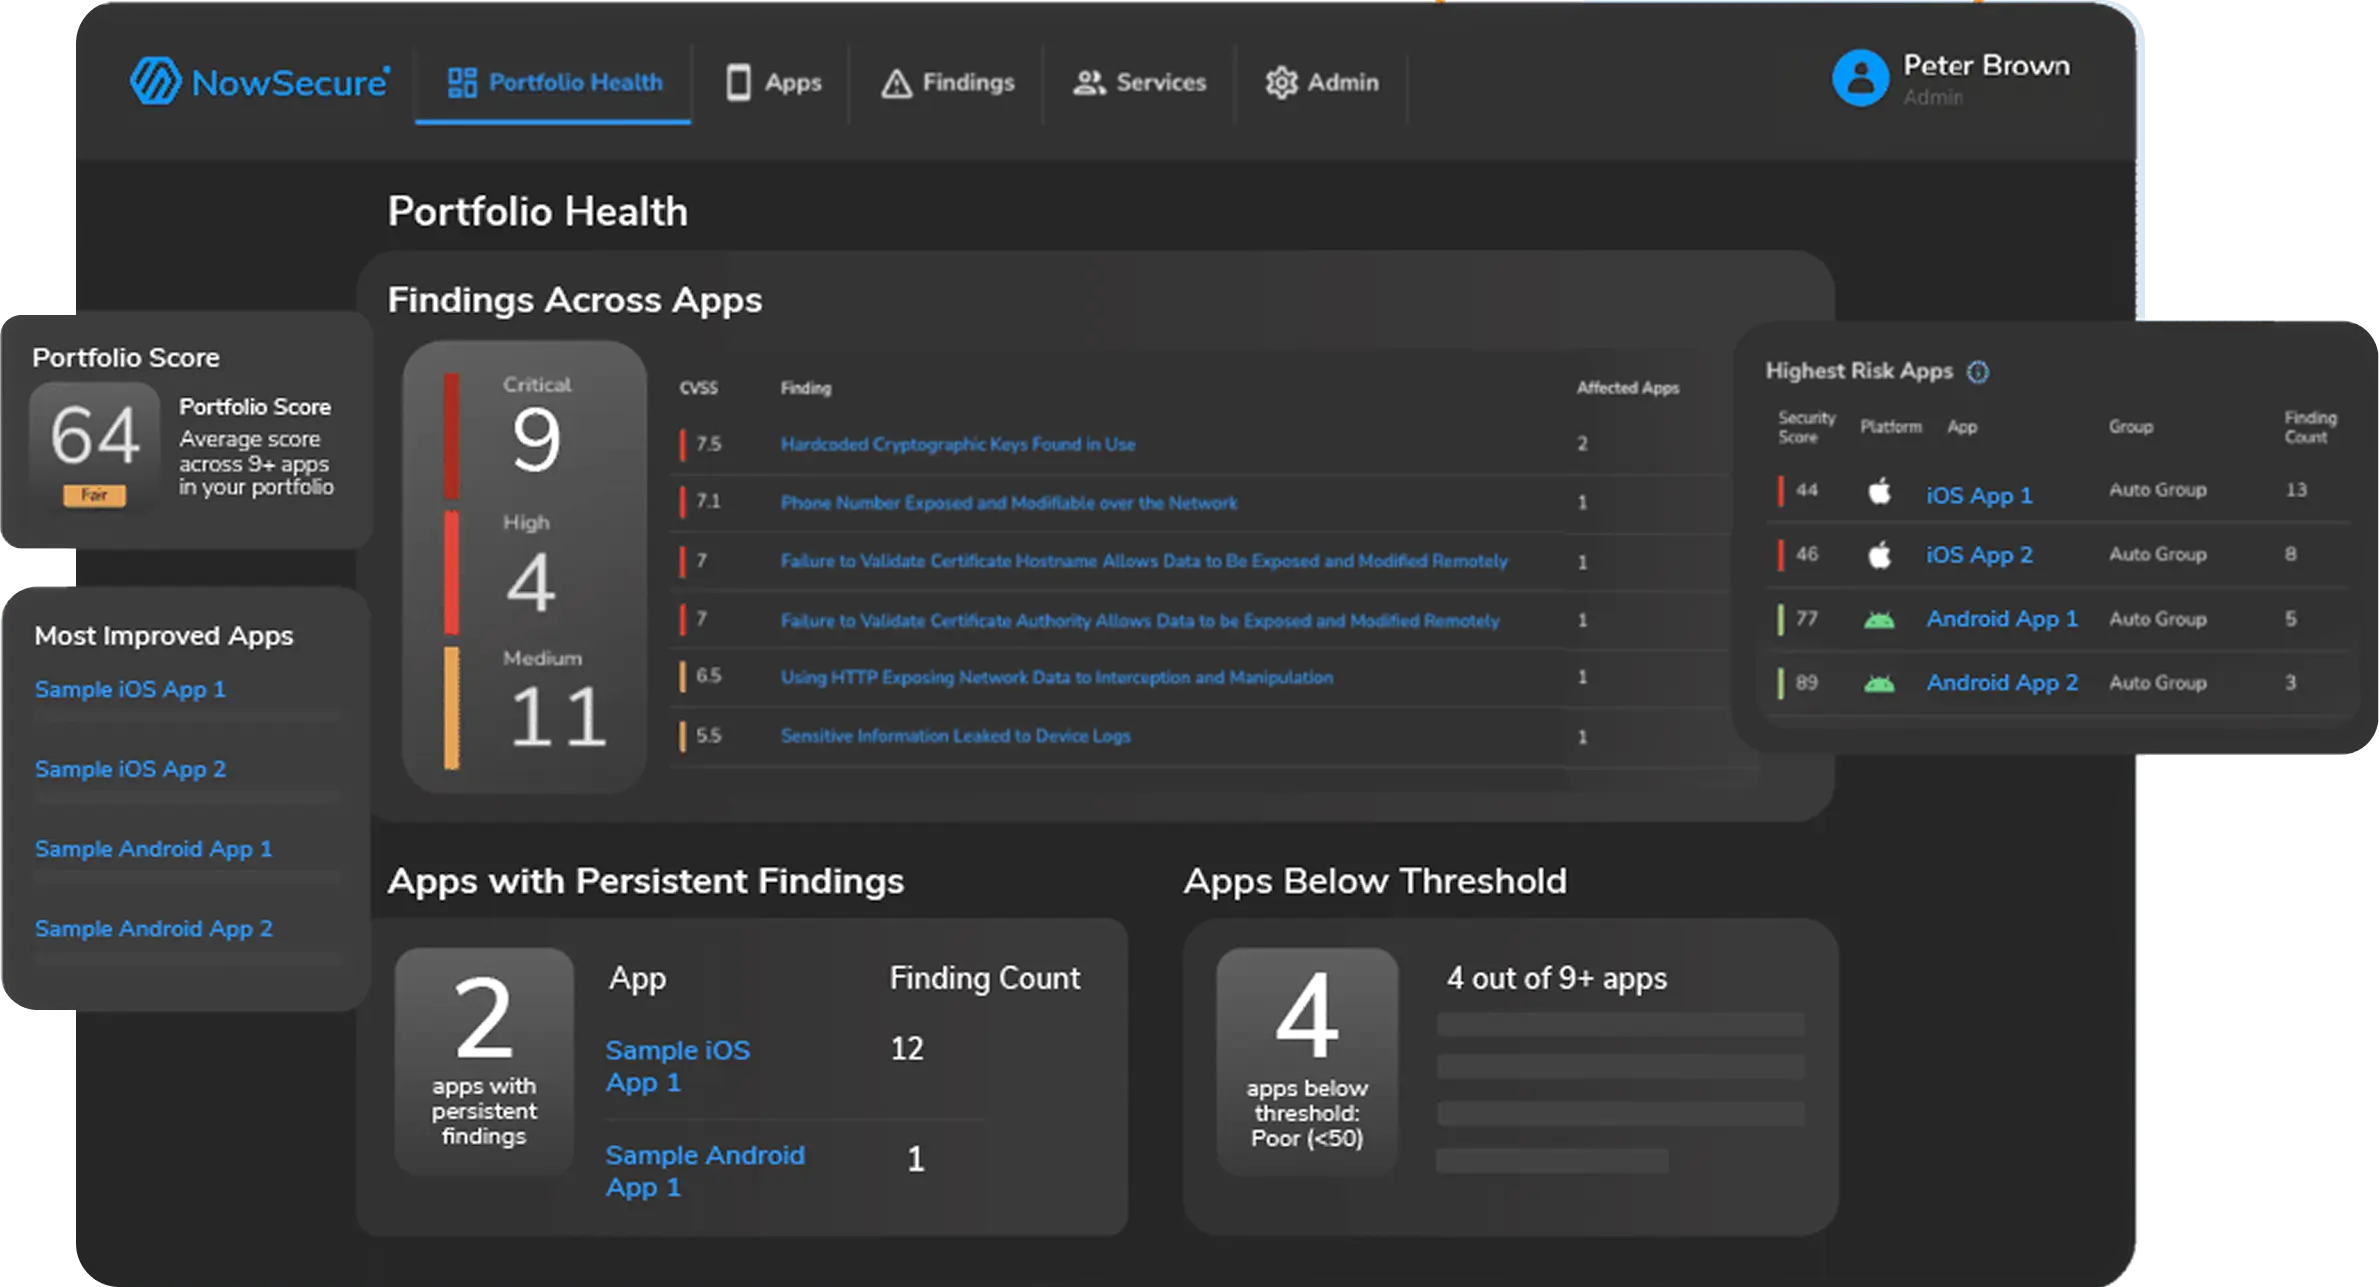
Resources
Mobile Application Risk Management Resources
Frequently asked questions about mobile application security testing
Have more questions? Get in touch with our team.