MOBILE Application SECURITY TESTING (MAST)
Mobile app security testing for the app your users actually install
Source-code scanners test what your developers wrote. NowSecure tests the compiled iOS and Android app on real devices, logged in, with every SDK and AI feature inside it, then hands developers findings backed by runtime evidence.
TRUSTED BY ENTERPRISE TEAMS THAT BUILD, SECURE, AND GOVERN MOBILE APPS
MAST EXPLAINED
What is mobile app security testing?
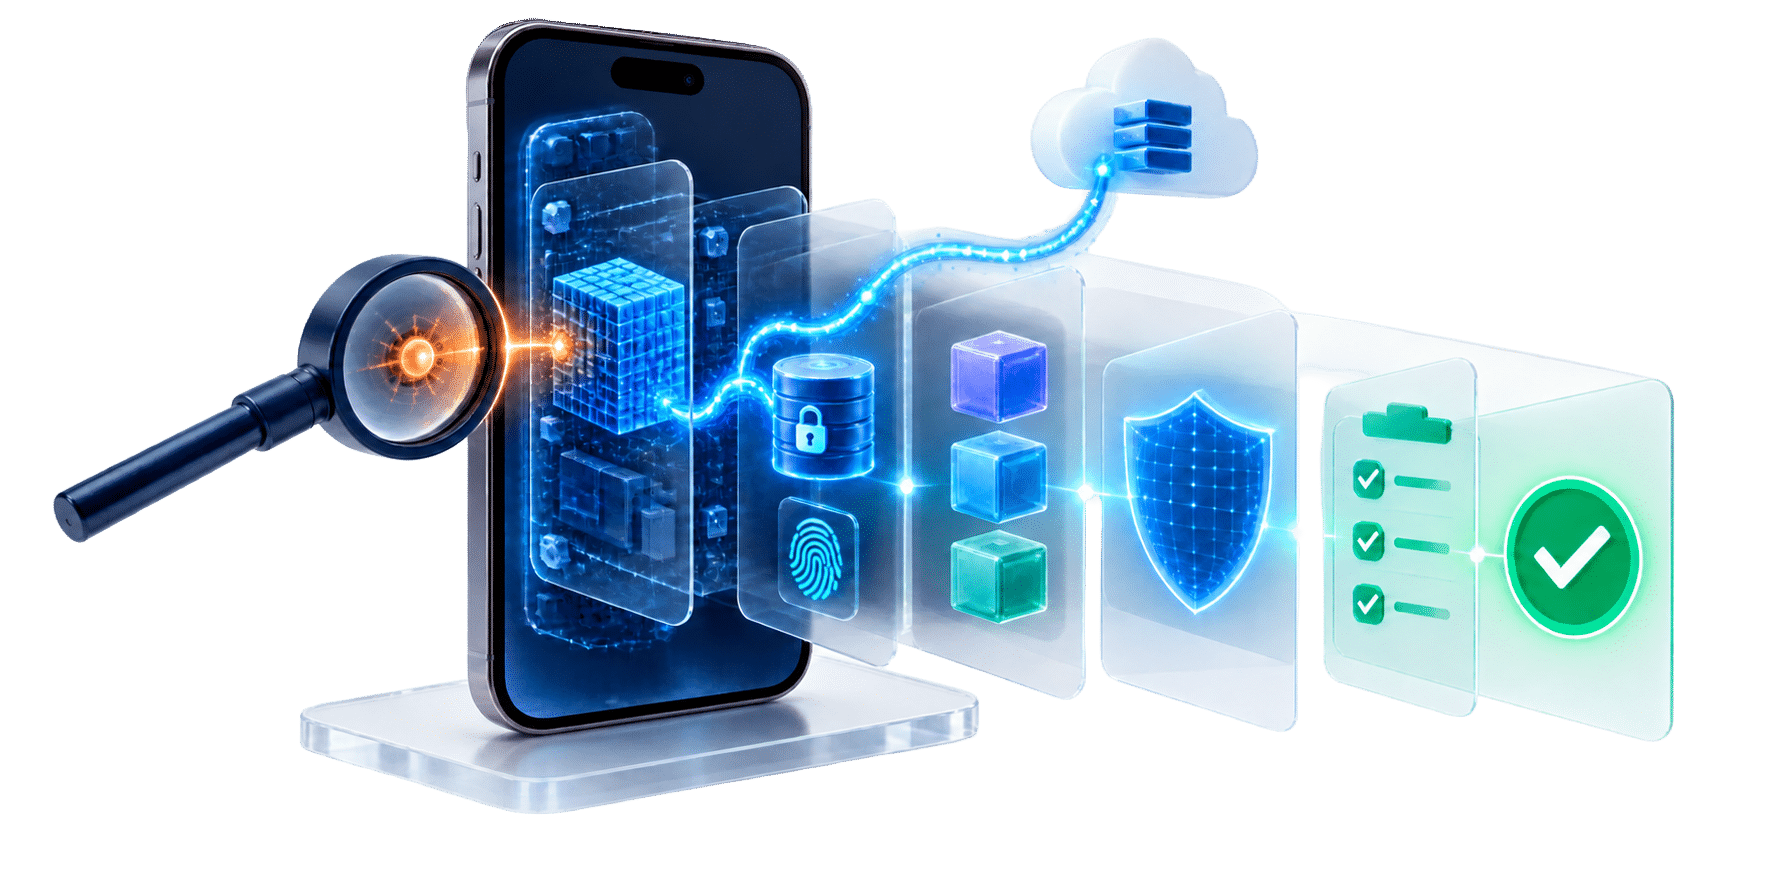
Mobile app security testing (MAST) is the process of finding security and privacy flaws in iOS and Android apps. It analyzes the compiled app binary, runs the app on a device to see how it stores data, handles logins, and talks to APIs, and inspects the third-party SDKs bundled inside it. OWASP MASVS defines the requirements a secure mobile app should meet, and the OWASP MASTG defines how to test against them.
MAST is its own category because mobile apps run on devices you do not control. Anyone can download your app, decompile it, attach a debugger, and watch its traffic. Testing that stops at the source code or at the API layer misses most of what that person would find.
WHAT MAST FINDS
What mobile app security testing finds that
source-code scanning misses
Testing behind the login is where most of the difference shows up. NowSecure research found that authenticated mobile app security testing finds 78% more sensitive data risk.
Where the risk lives
The compiled binary
What goes wrong
Hardcoded keys, exposed endpoints, and weak build settings in the shipped app.
How NowSecure Tests it
Static and binary analysis of the IPA or APK you actually ship.
Where the risk lives
Third-party SDKs
What goes wrong
Analytics, ad, and payment SDKs sending data your team never approved.
How NowSecure Tests it
Where the risk lives
Behind the login
What goes wrong
Session, token, and account data flows that unauthenticated scans never reach.
How NowSecure Tests it
Where the risk lives
Local storage
What goes wrong
Session tokens or personal data left in logs, caches, or unprotected storage.
How NowSecure Tests it
Dynamic analysis on real iOS and Android devices, not emulators.
Where the risk lives
Network and APIs
What goes wrong
Weak TLS, bypassable certificate pinning, and data sent to the wrong endpoint.
How NowSecure Tests it
Traffic captured from the app's side through the authenticated session.
Where the risk lives
AI features
What goes wrong
Prompts, user data, or model traffic sent to third-party AI services.
How NowSecure Tests it
HOW MAST COMPARES
MAST vs. SAST, DAST, and penetration testing
Most mobile programs need MAST on every build and mobile app penetration testing on the releases that carry the most risk.
| Approach | What it tests | Where it falls short for mobile | Where it fits |
|---|---|---|---|
| SAST | Source code in the repository | Never sees the compiled app, bundled SDKs, or runtime behavior | Code-level checks in pull requests |
| Web DAST | A running web app or API, from the outside | Cannot run a mobile app, bypass pinning, or inspect on-device storage | Backend and API testing |
| MAST | The compiled mobile app, both statically and running on a device | Automation does not replace a human tester for novel business logic abuse | Every build, in CI/CD |
| Mobile pen testing | The app, attacked by a skilled human tester | Too slow and costly to run on every build | Major releases, high-risk apps, and compliance |
FROM BUILD TO FIX
How NowSecure mobile app security testing works
The NowSecure Platform takes every build from upload to fix in five steps.

Connect a build
Upload an IPA or APK, or trigger tests automatically from GitHub Actions, GitLab, Azure DevOps, Jenkins, CircleCI, or Bitrise.

Analyze the binary
Static and binary analysis maps the app's code, libraries, SDKs, and embedded secrets.

Run it on real devices
Dynamic analysis exercises the app on physical iOS and Android hardware, logs in with AI-Navigator, and captures runtime behavior and network traffic.

Correlate and report
Findings are mapped to OWASP MASVS, checked against both static and dynamic evidence, and sent to your tracker with remediation guidance.

Go deeper where it matters
Add Guided Testing or Pen Testing as a Service when an app needs an analyst to work through MFA
All of this runs on the NowSecure Platform.
EVIDENCE WITH EVERY FINDING
Findings your developers will act on
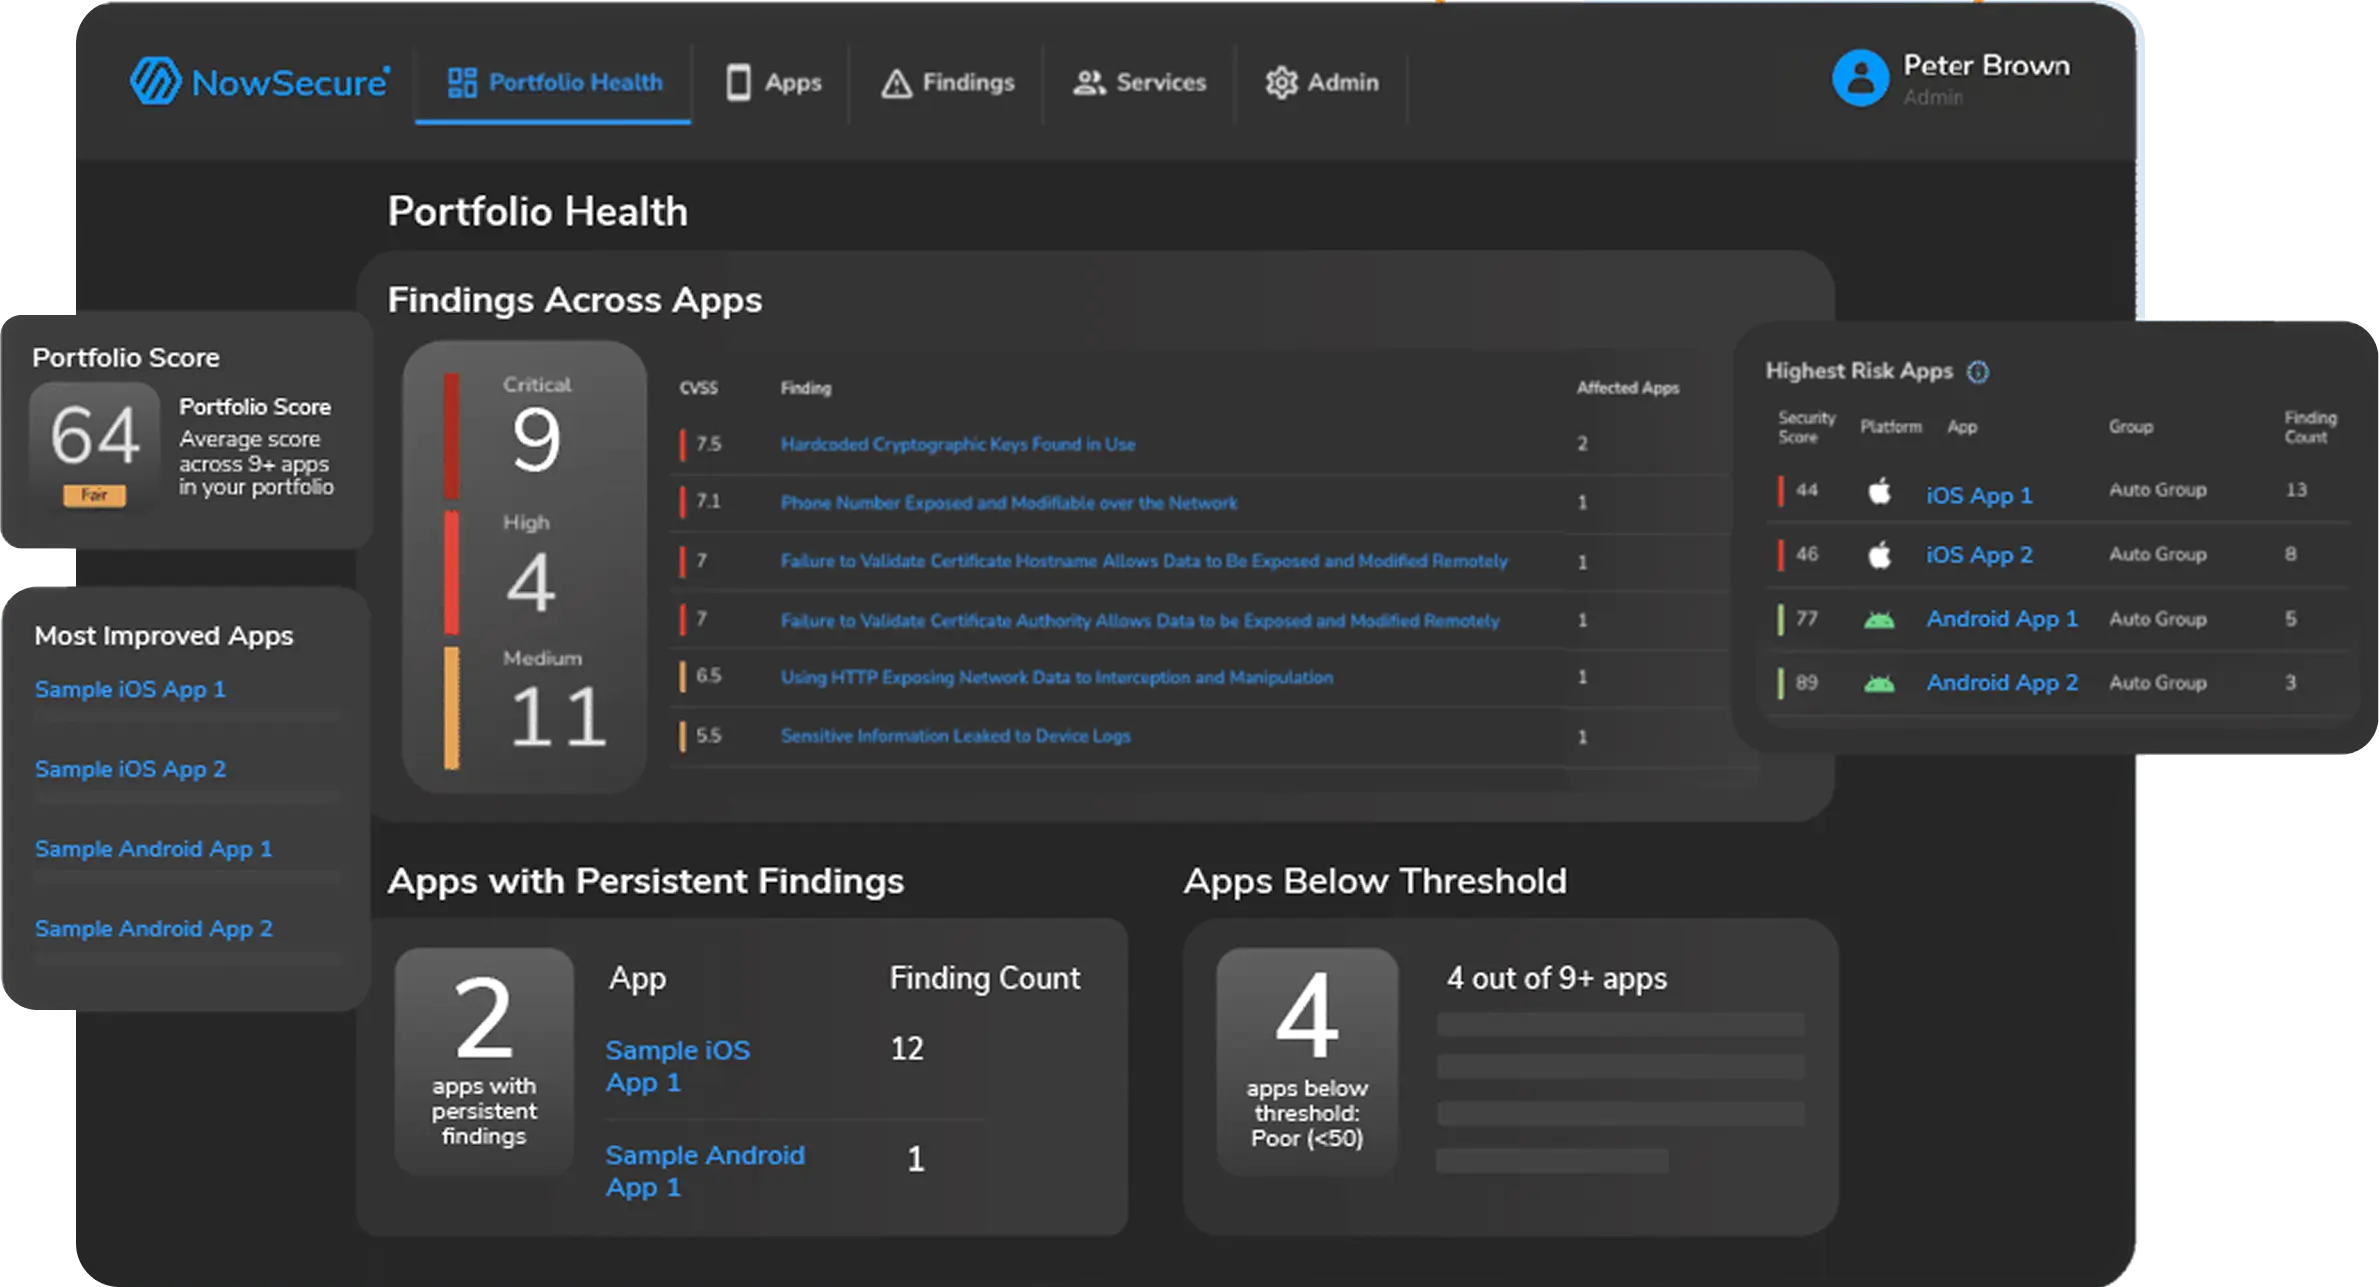
A security tool that floods the backlog gets switched off. Every NowSecure finding ships with the evidence that produced it: the file in the binary, the runtime behavior, or the captured request. It also includes the MASVS requirement it maps to and a fix your developers can apply. Teams set risk-based release policies, so only findings above their threshold block a build.
Tickets include remediation suggestions from NowSecure which are very, very helpful.
Micha Katz, Chief Information Security Officer, Yellow Card
See what NowSecure finds in your app
Bring one of your iOS or Android apps to a demo. We'll show you what turns up in the binary, on a real device, and behind the login.
DevSecOps Integration
Mobile app security testing in your
DevSecOps pipeline
Mobile apps change with every release: new features, updated SDKs, new AI services. NowSecure runs in the pipeline you already use, so every build is tested before it ships.
What gets retested on every build:

New application builds

Updated functionality

Changed security controls

Third-party SDK updates

Application behavior changes
Where testing runs in your lifecycle:
Software Supply Chain
Third-party SDK and software supply chain testing
Analytics, advertising, payment, and AI SDKs become part of the app you ship, running with the same access to user data as your own code. NowSecure identifies every component inside the compiled app and watches what each one does at runtime.
What SDK analysis shows you:
Which SDKs and libraries are inside your app
Which components have known vulnerabilities

What app data and device capabilities each SDK can access

Where SDKs send data outside your app
Get a full inventory of every component in your app with a dynamic mobile SBOM.
Emerging Risk
Security testing for AI features in mobile apps
Mobile apps now embed AI models, call third-party AI services, and send user prompts off the device, sometimes through SDKs your security team has not reviewed. NowSecure identifies the AI inside your app and shows what data reaches it.
What AI testing looks for:
Sensitive data exposed to AI features
New network paths to AI services
Third-party AI SDKs and models
App behavior changed by AI features
Missing security controls around AI features
See the AI in your apps with NowSecure AI detection and AI security governance.
Open standards, open source
Open standards, open source
NowSecure helps write the OWASP mobile standards it tests against. Carlos Holguera, a NowSecure principal research engineer, co-leads the OWASP Mobile Application Security project that maintains MASVS and MASTG.
See how each MASVS domain is covered in the OWASP mobile app security testing overview and on the mobile standards and compliance page.
The NowSecure Difference
Trusted by teams that ship mobile apps at scale

T-Mobile
Protects the apps that connect 130 million customers.

Warner Bros. Discovery
Builds blockbuster mobile security across its streaming and entertainment apps.

DeepSeek iOS app
NowSecure research uncovered multiple security and privacy flaws in the DeepSeek iOS app.

Bell Canada
Dials into mobile app risk management.
Test the app your users actually install
Get a demo built around your apps, your pipeline, and your release schedule.
Resources
Mobile app security testing resources